AWS User Group Kyrgyzstan Meetup · Bishkek · 12 April 2023
AppSec Supply Chain Security with AWS
Software supply chain security in the cloud: why open-source components became the main attack point and how to build SCA into the development process on AWS.
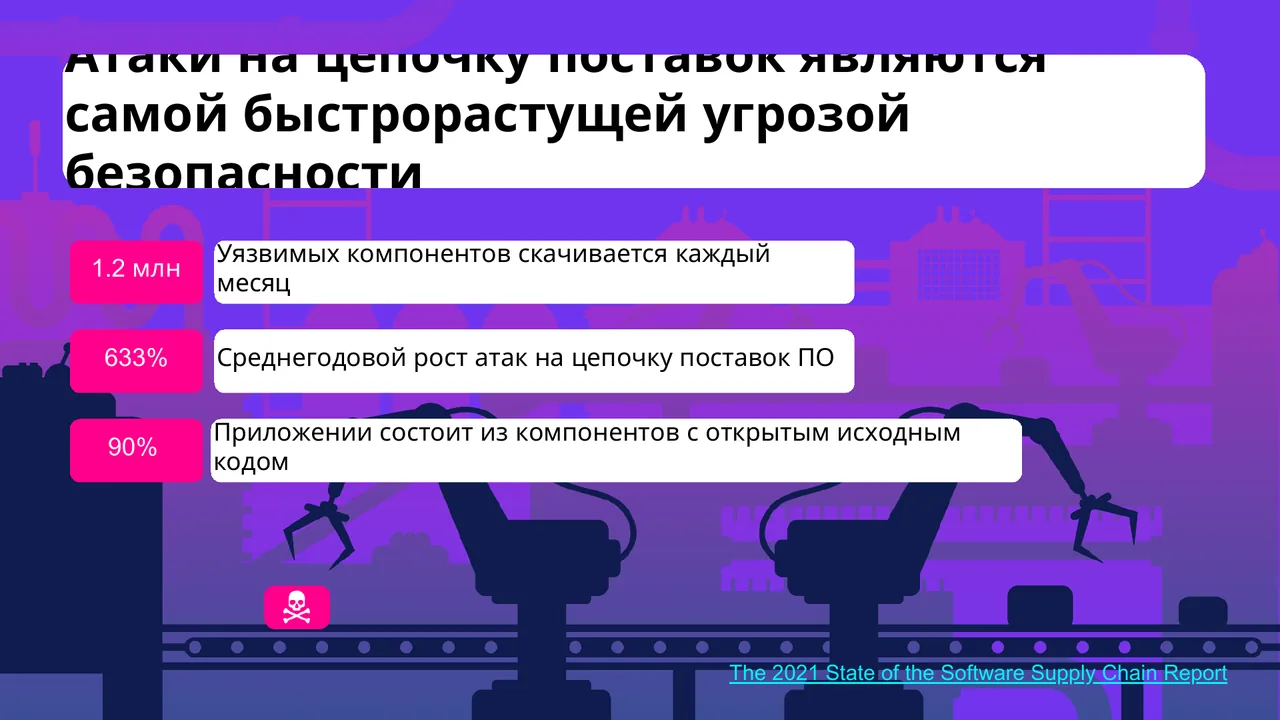
Supply chain attacks are the fastest-growing threat: 1.2 million vulnerable components are downloaded every month, attacks grow 633% a year (State of the Software Supply Chain 2021).
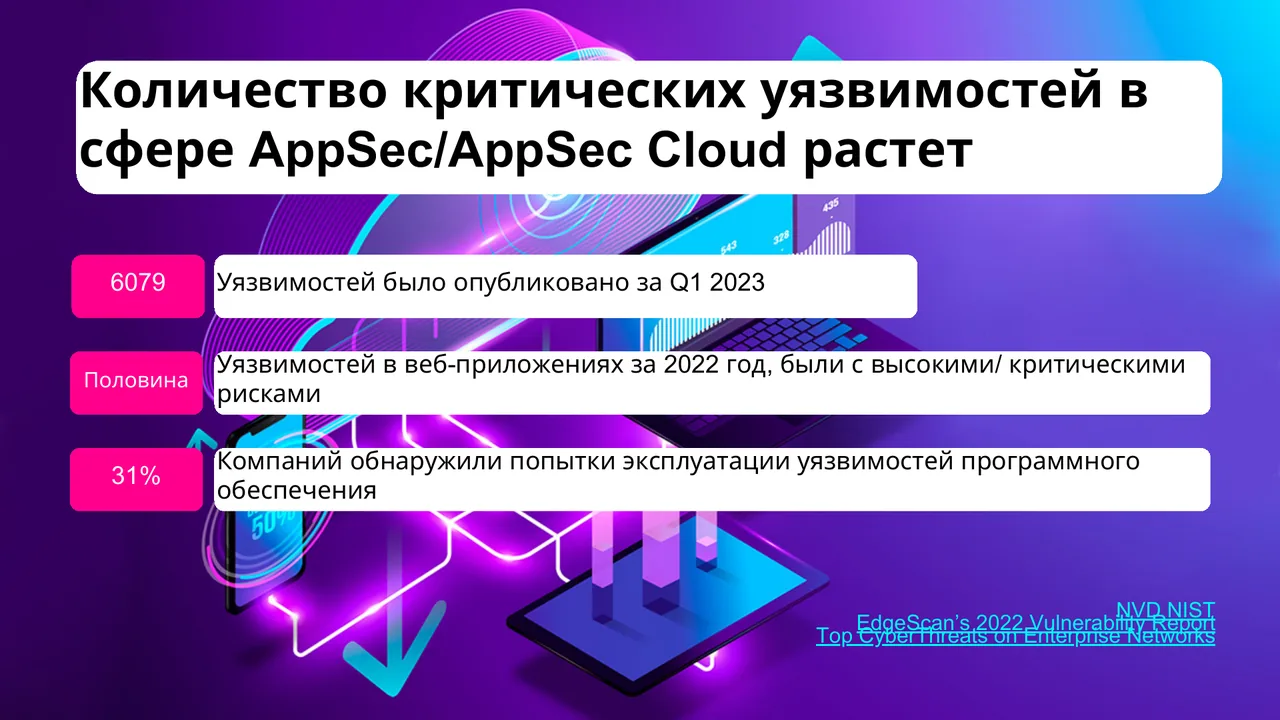
The number of critical vulnerabilities is growing: 6079 were published in Q1 2023 (NVD).
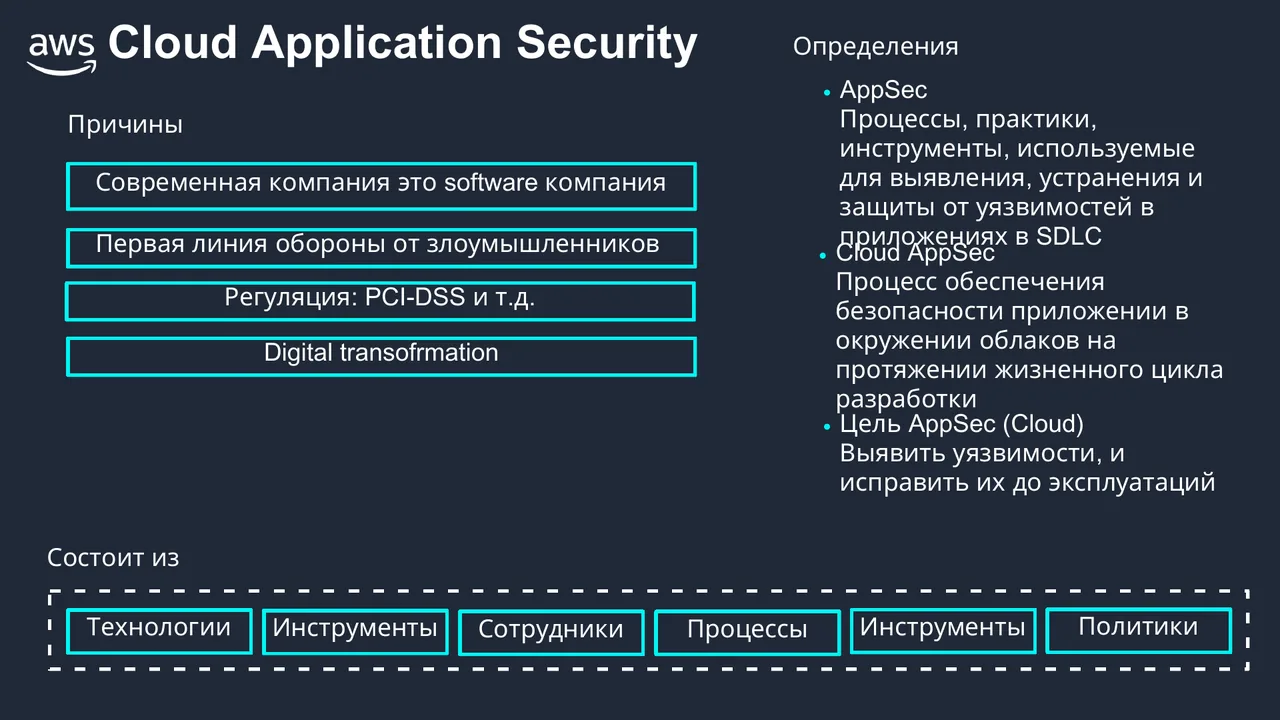
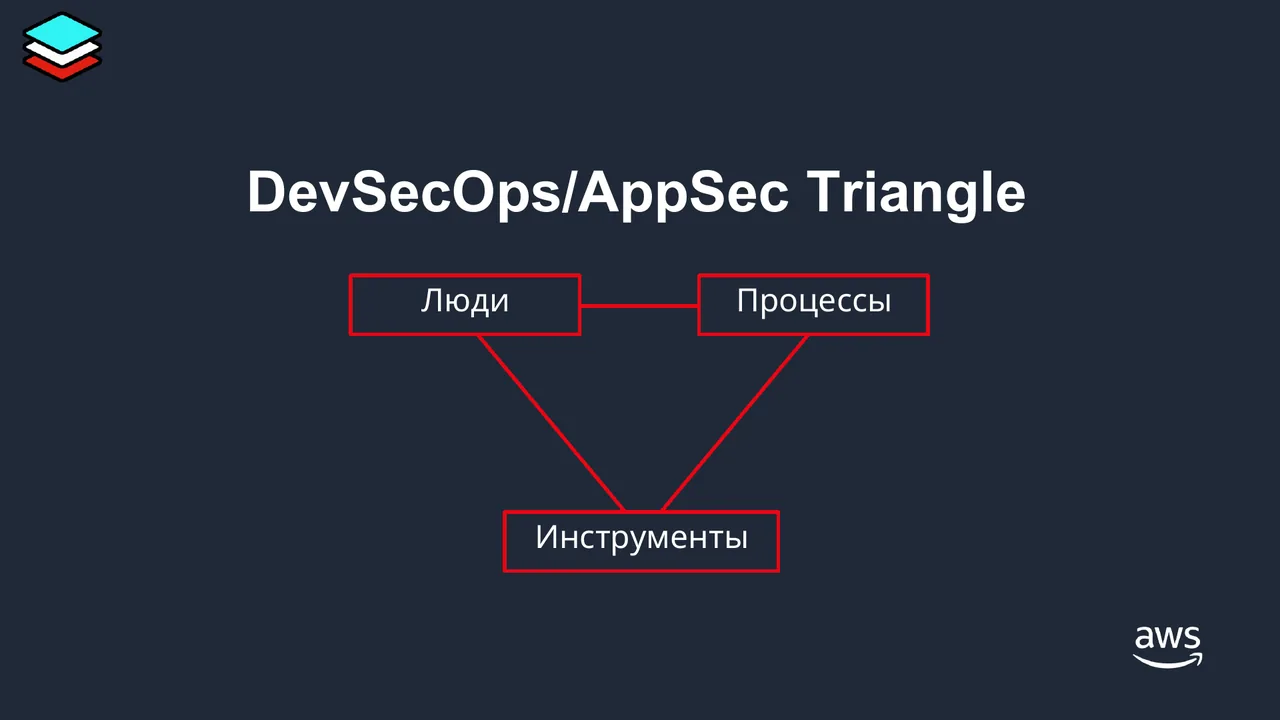
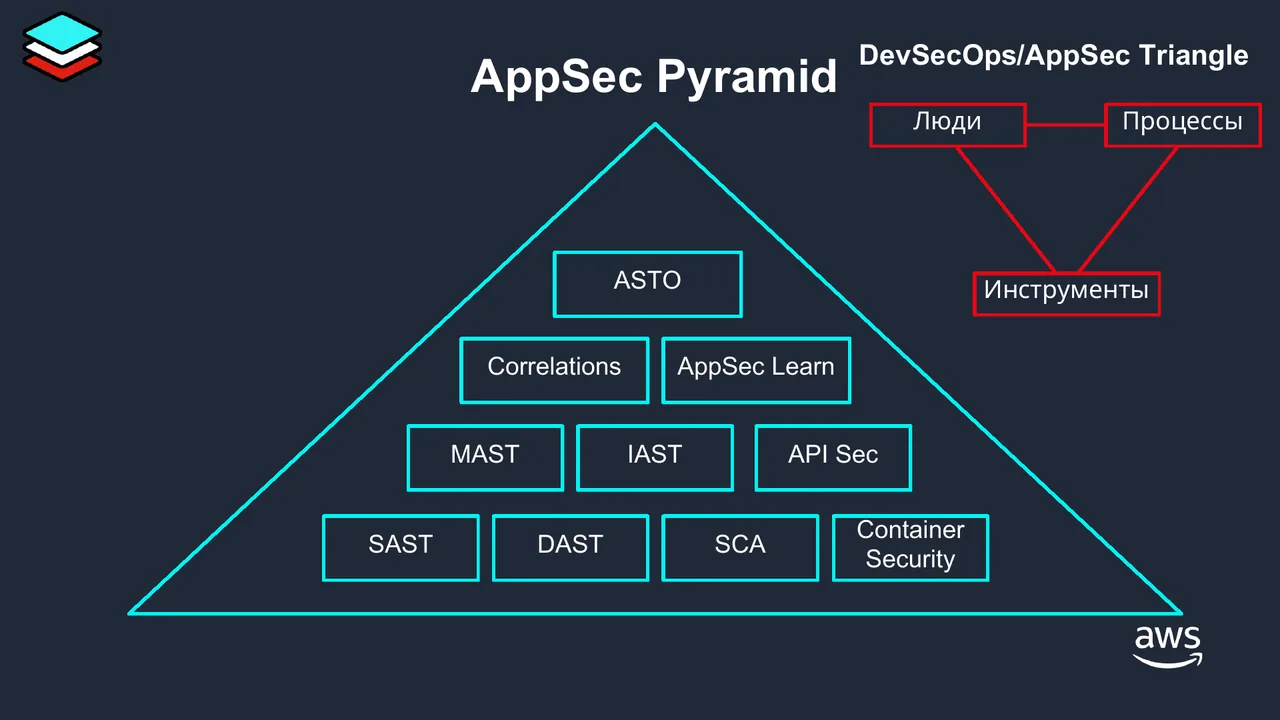
AppSec and Cloud AppSec: definitions, the "people, processes, tools" triangle, the AppSec pyramid.
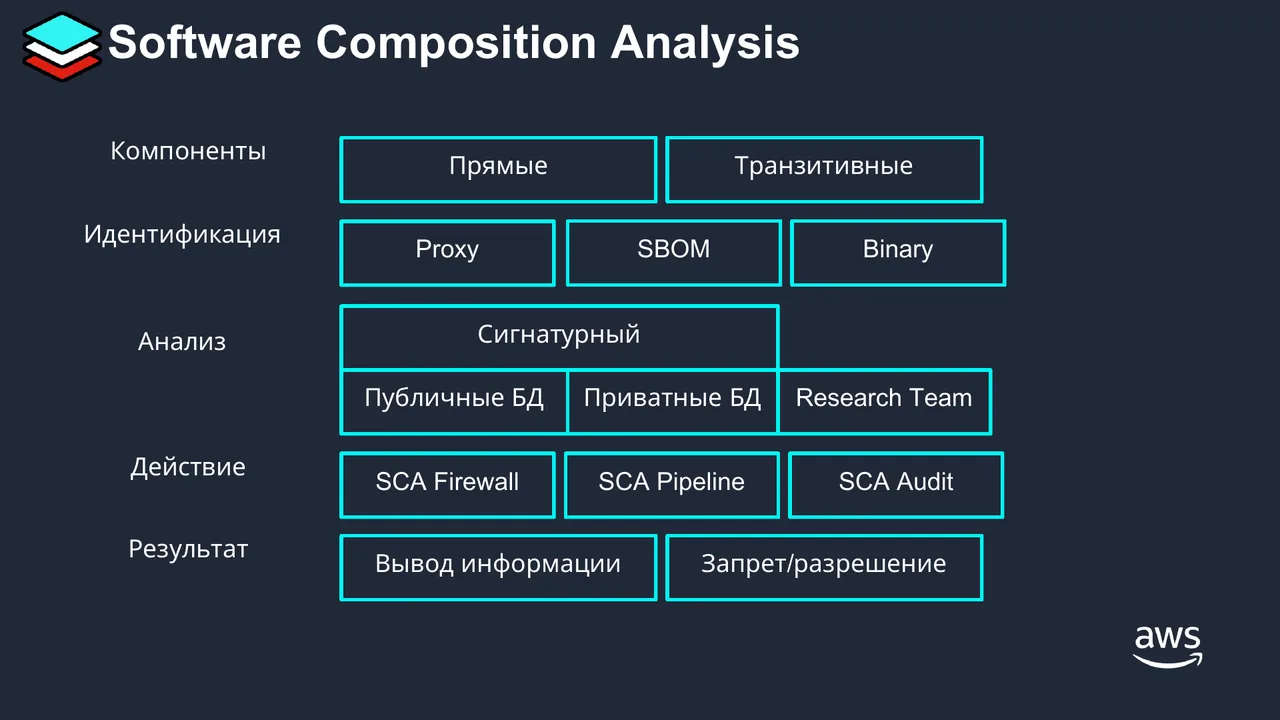
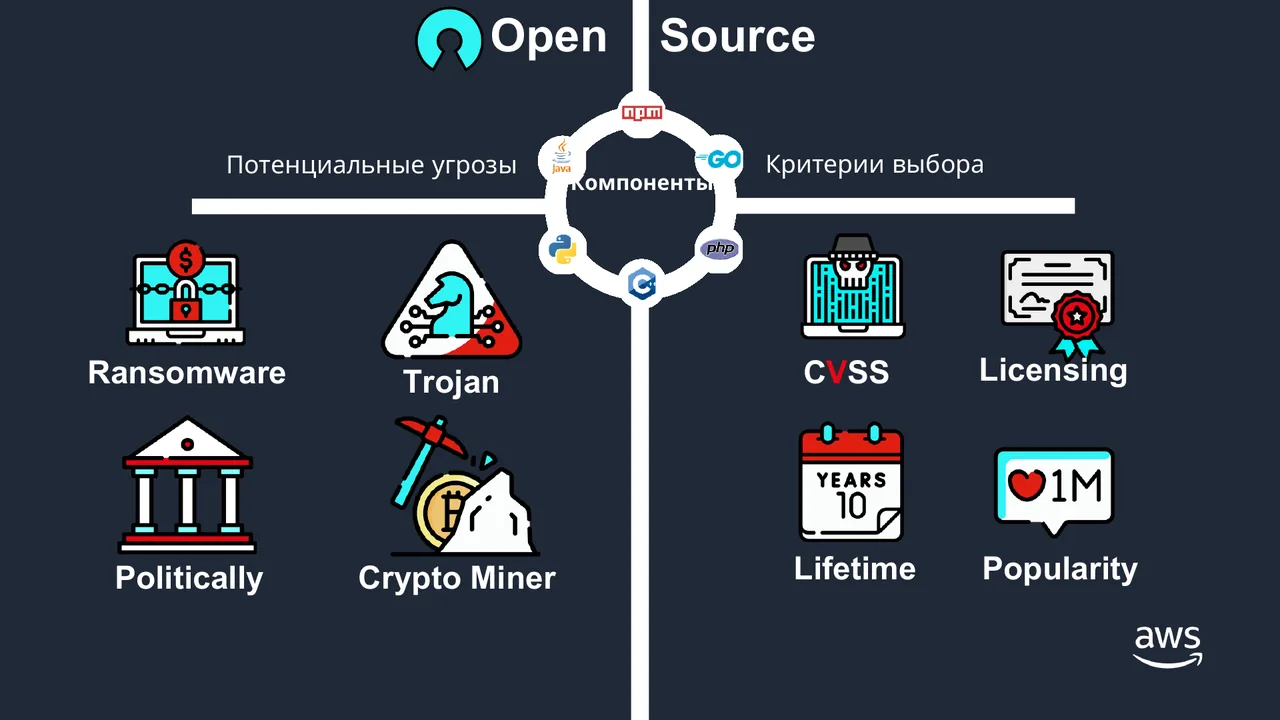
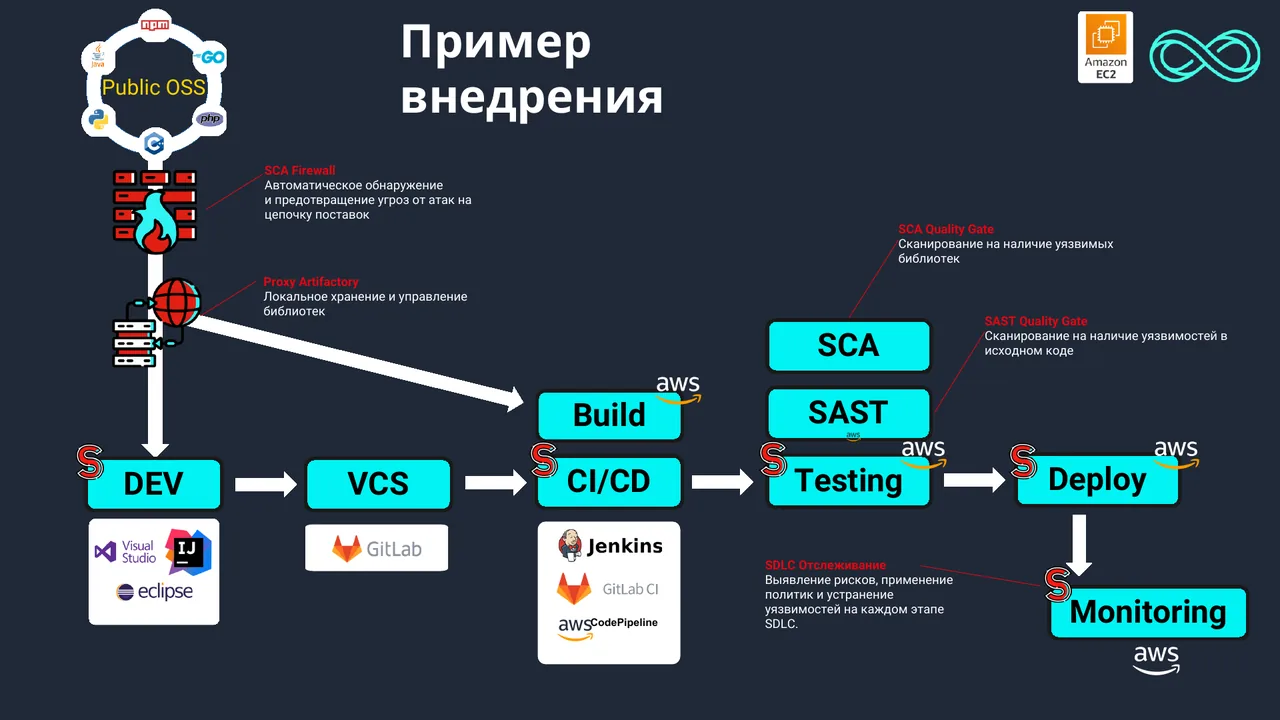
How SCA works: direct and transitive dependencies, proxy, SBOM, SCA Firewall, pipeline check and audit; criteria for choosing components.
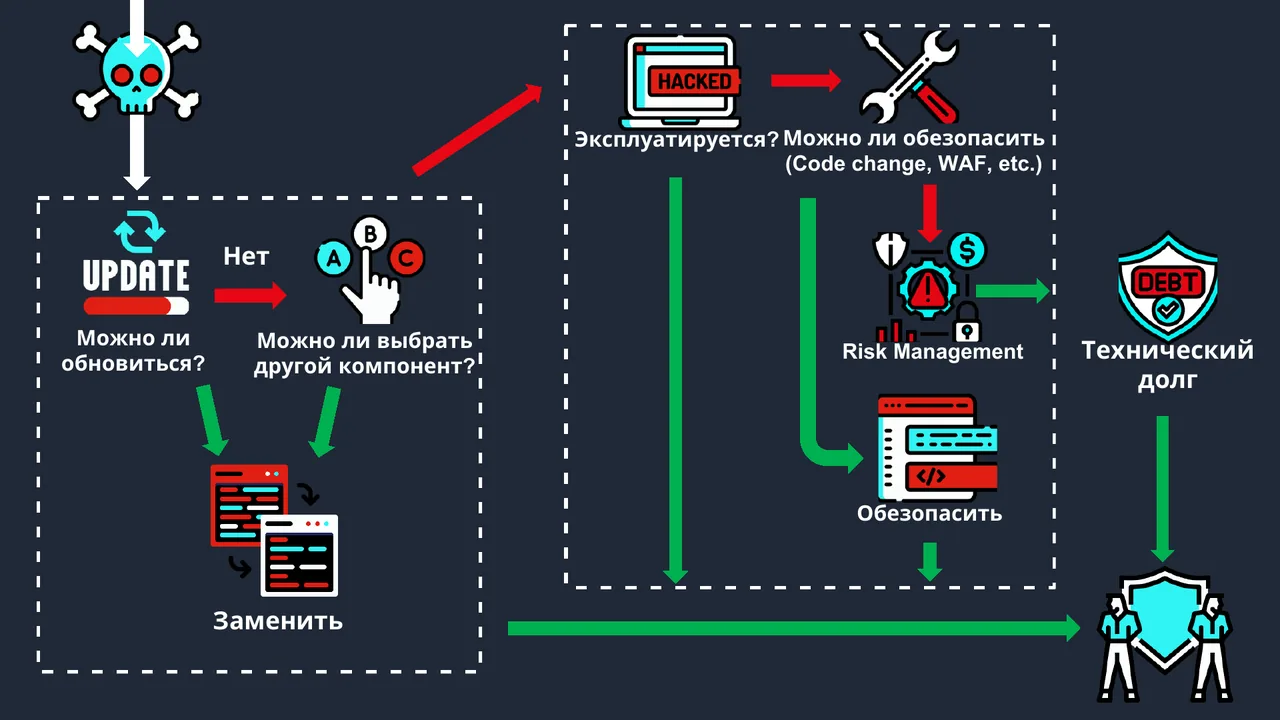
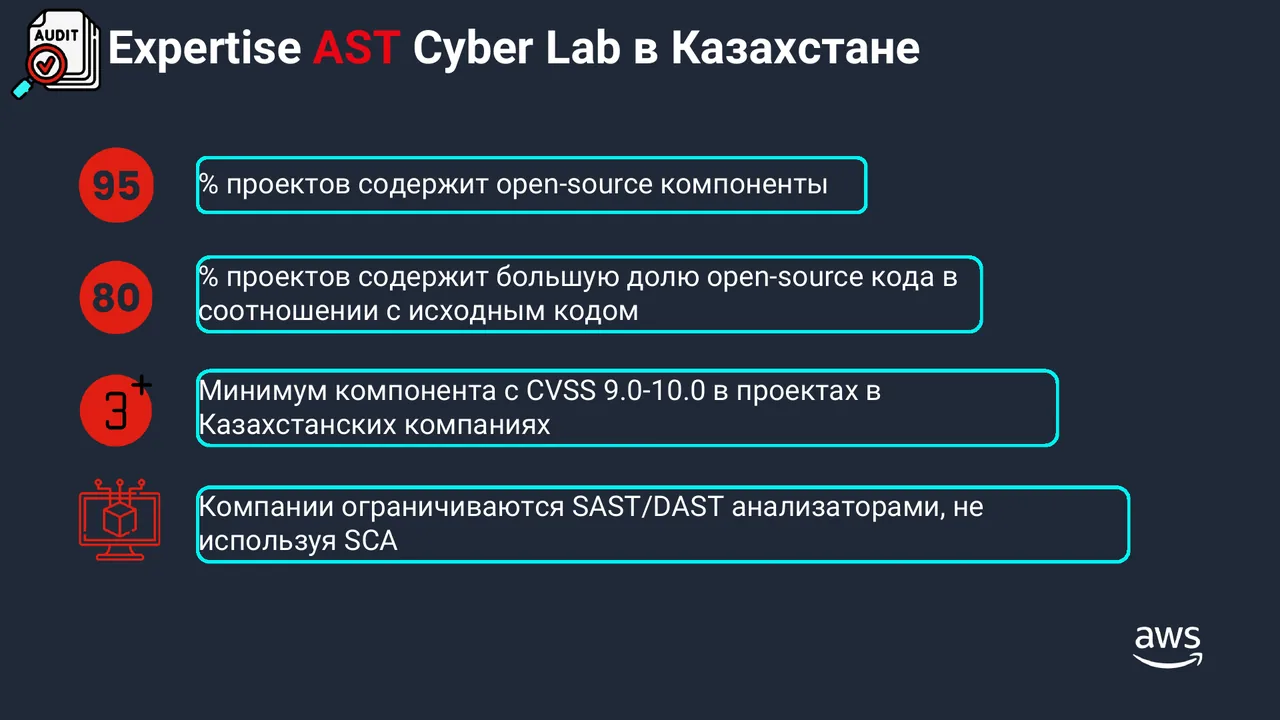
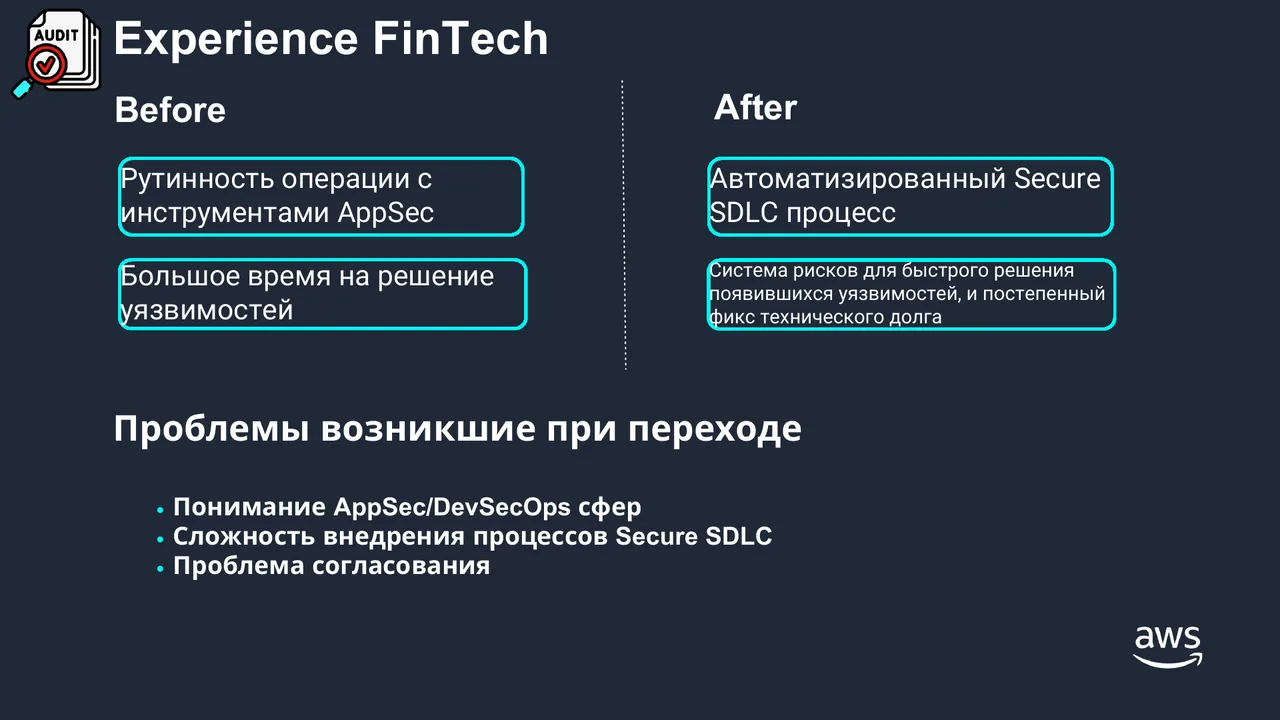
The experience of AST Cyber Lab in Kazakhstan and a fintech case: from routine to an automated Secure SDLC with a risk system and gradual work through technical debt.
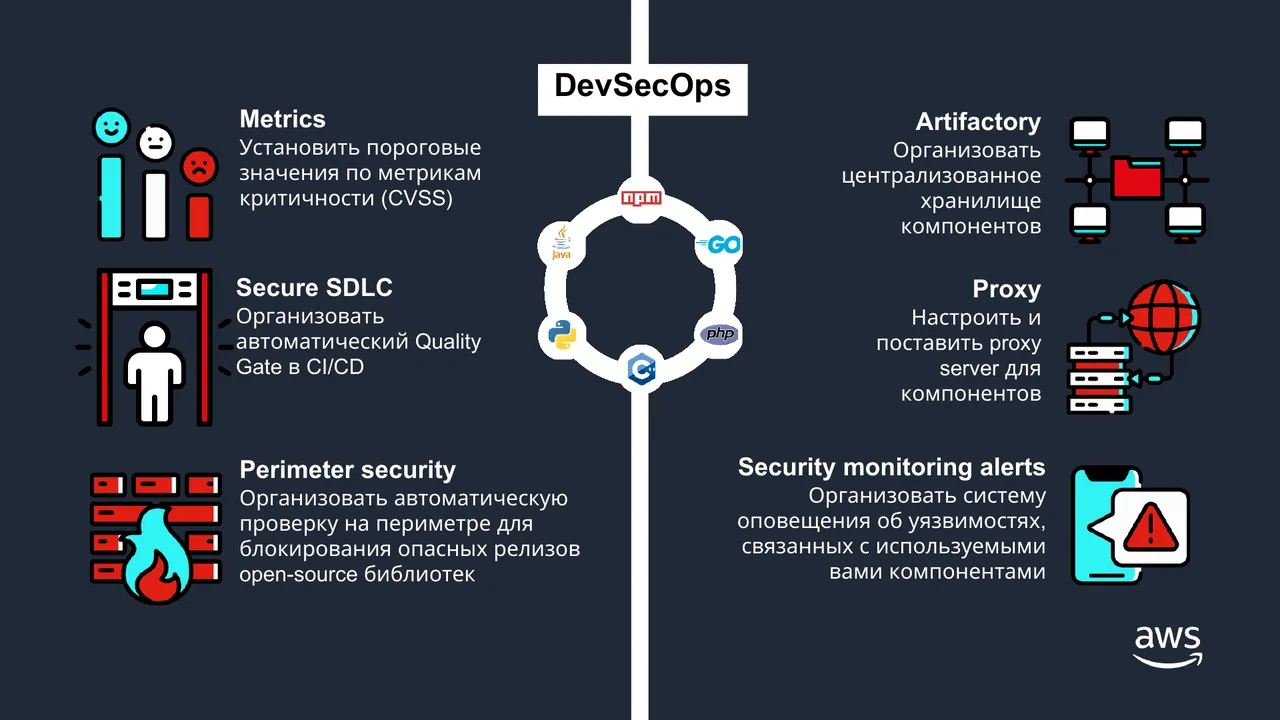
An implementation example in AWS CodePipeline: SCA Firewall, proxy repository, Quality Gate for SCA and SAST, risk tracking at every stage.