DevOpsDays Almaty 2022 · Almaty · 11 November 2022
Software supply chain protection
Why and how to protect against vulnerabilities in open-source components: from high-profile supply chain attacks to SCA built into the DevSecOps process.
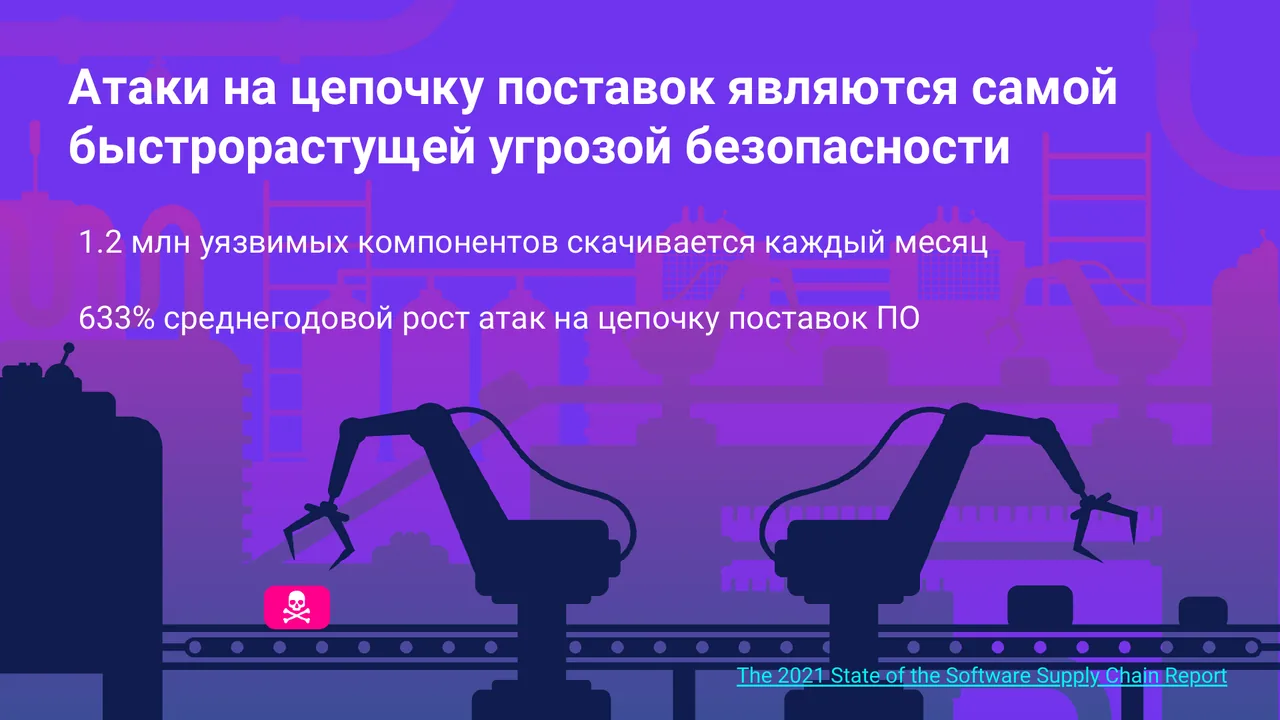
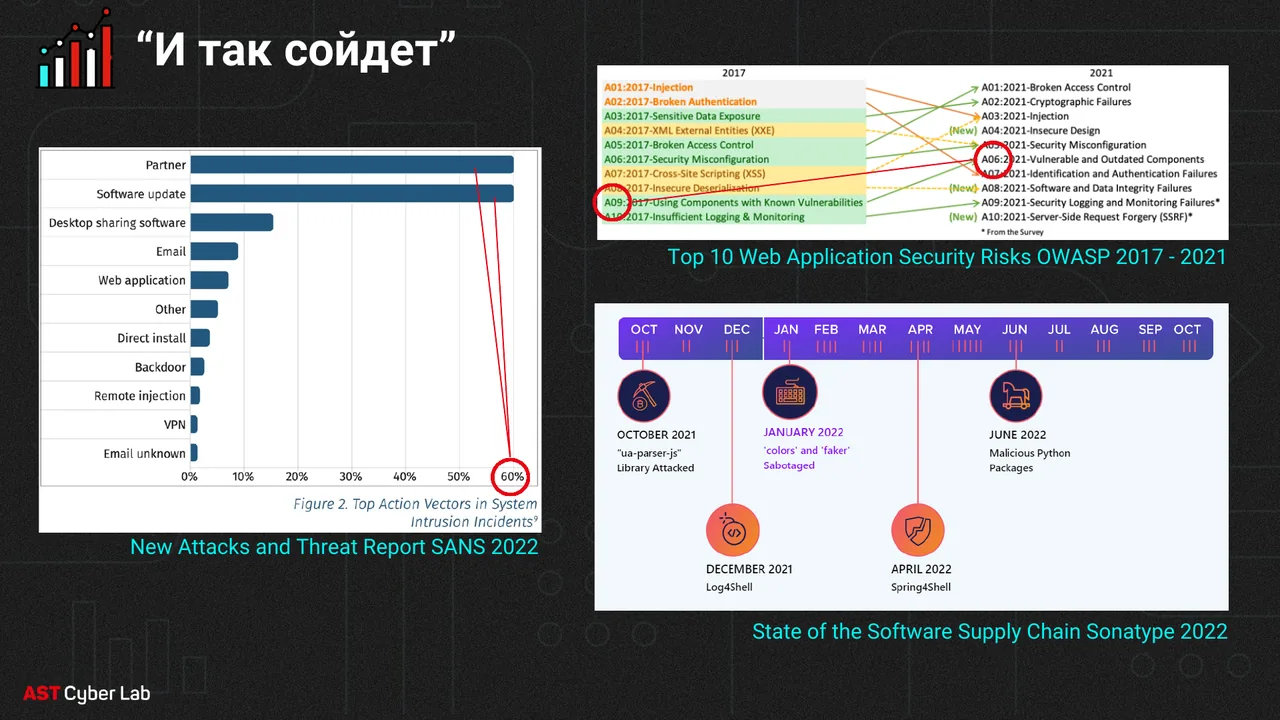
Supply chain attacks are the fastest-growing threat: 1.2 million vulnerable components are downloaded every month, attacks grow 633% a year (State of the Software Supply Chain 2021).
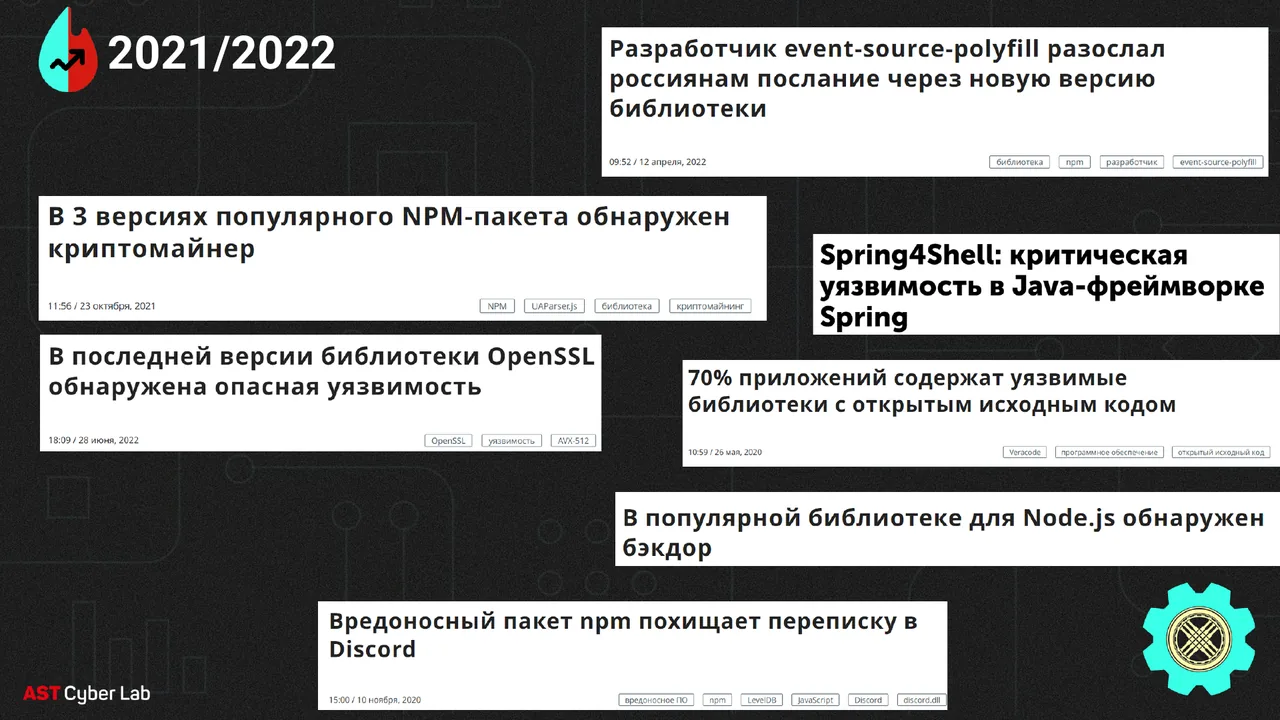
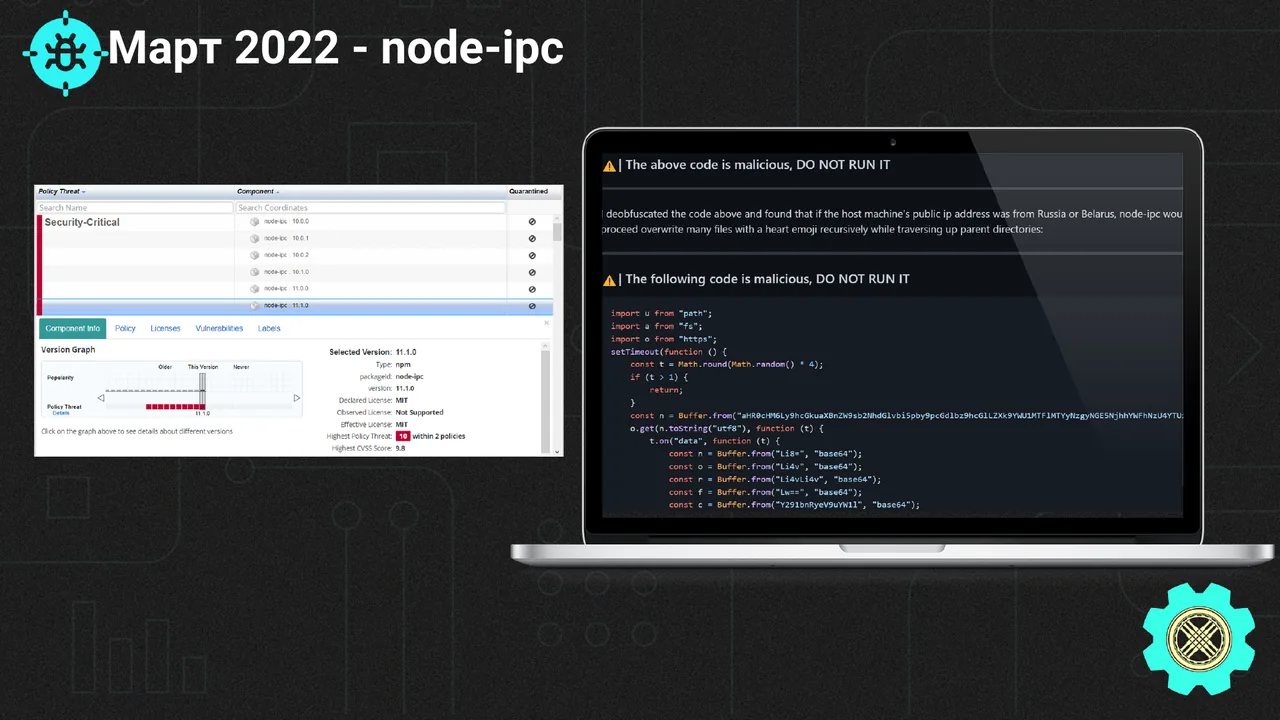
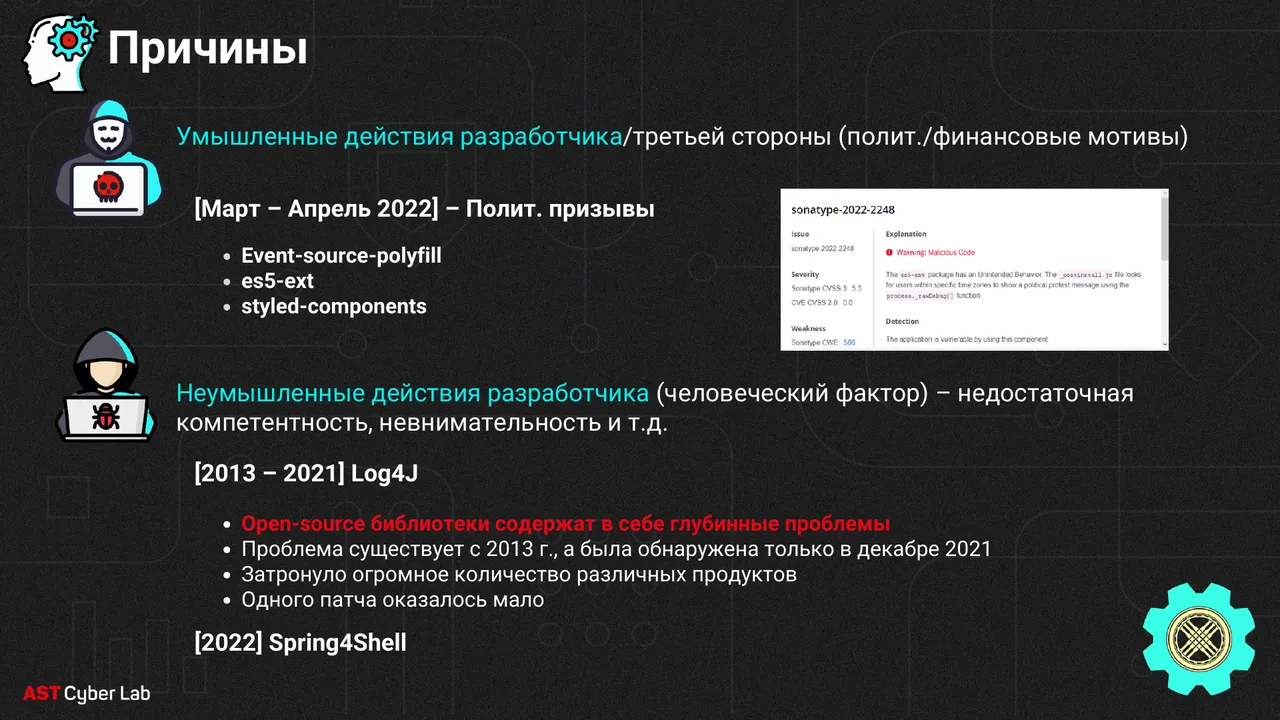
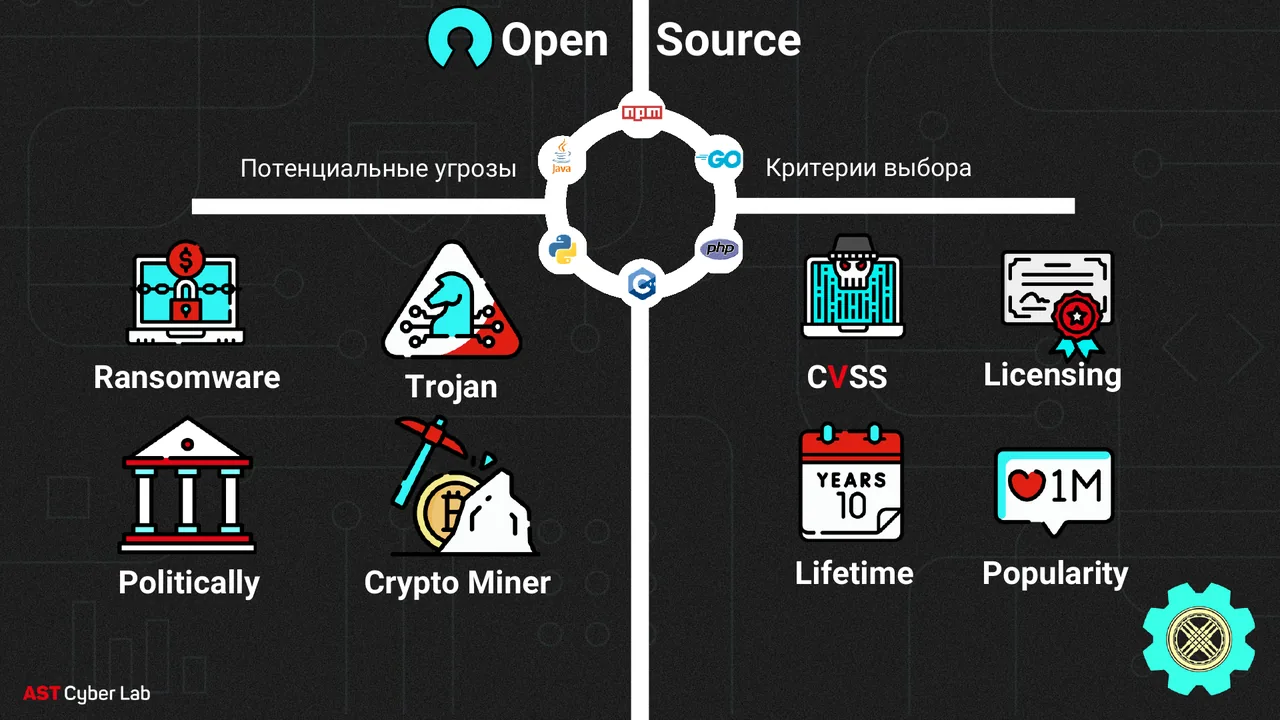
Cases of 2021–2022: a cryptominer in UAParser.js, the protestware node-ipc and event-source-polyfill, Spring4Shell, Log4j, malicious npm packages.
Why this happens: deliberate actions of developers and third parties, and the human factor.
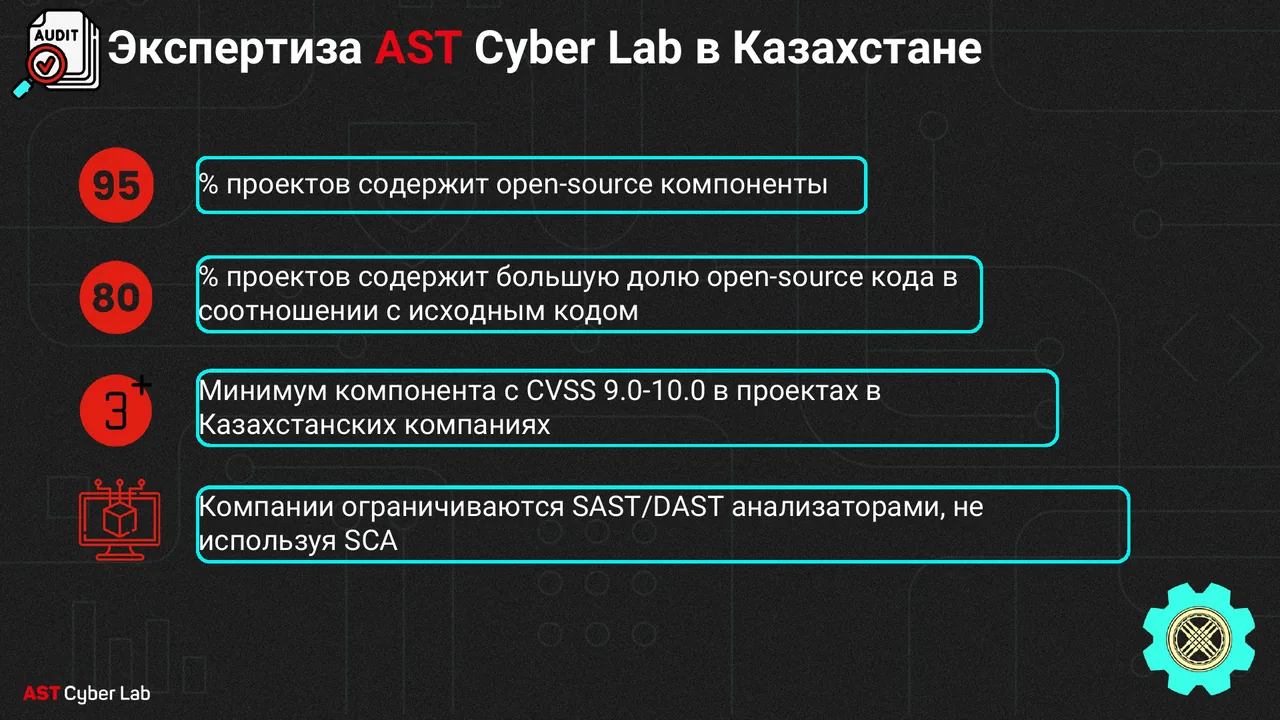
The experience of AST Cyber Lab in Kazakhstan: open-source components are present in 95% of projects, and many companies limit themselves to SAST and DAST without SCA.
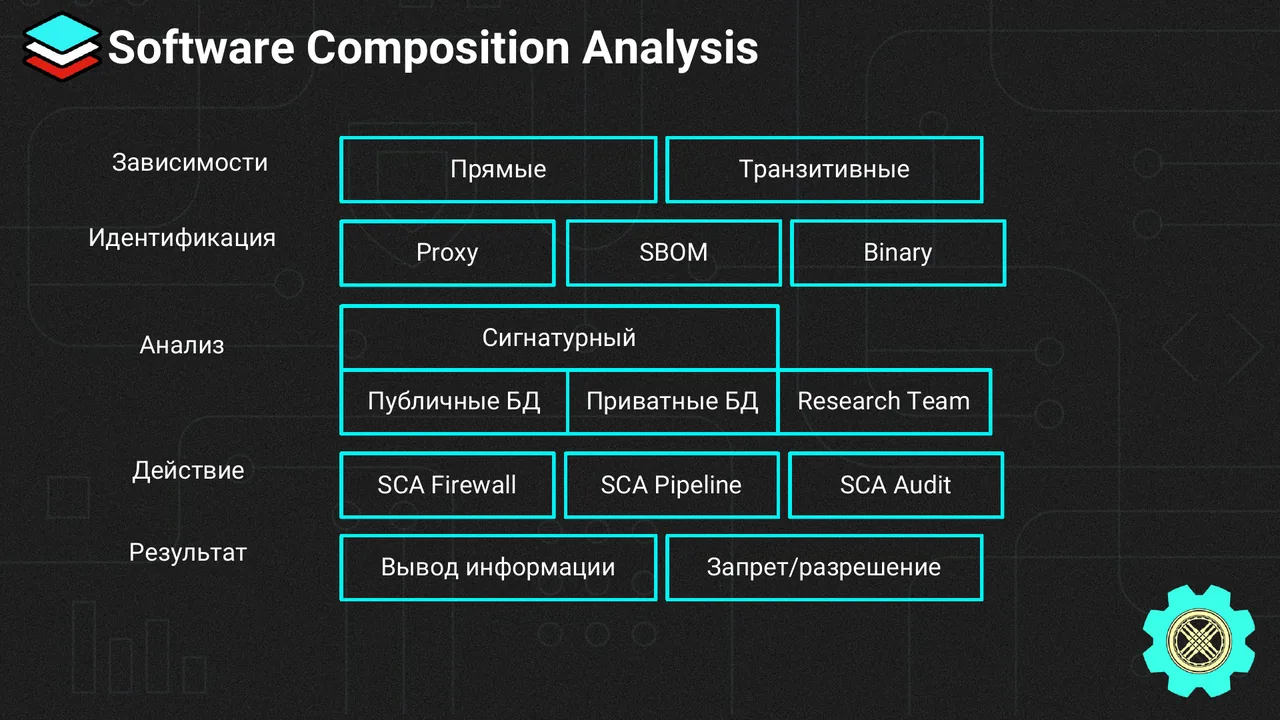
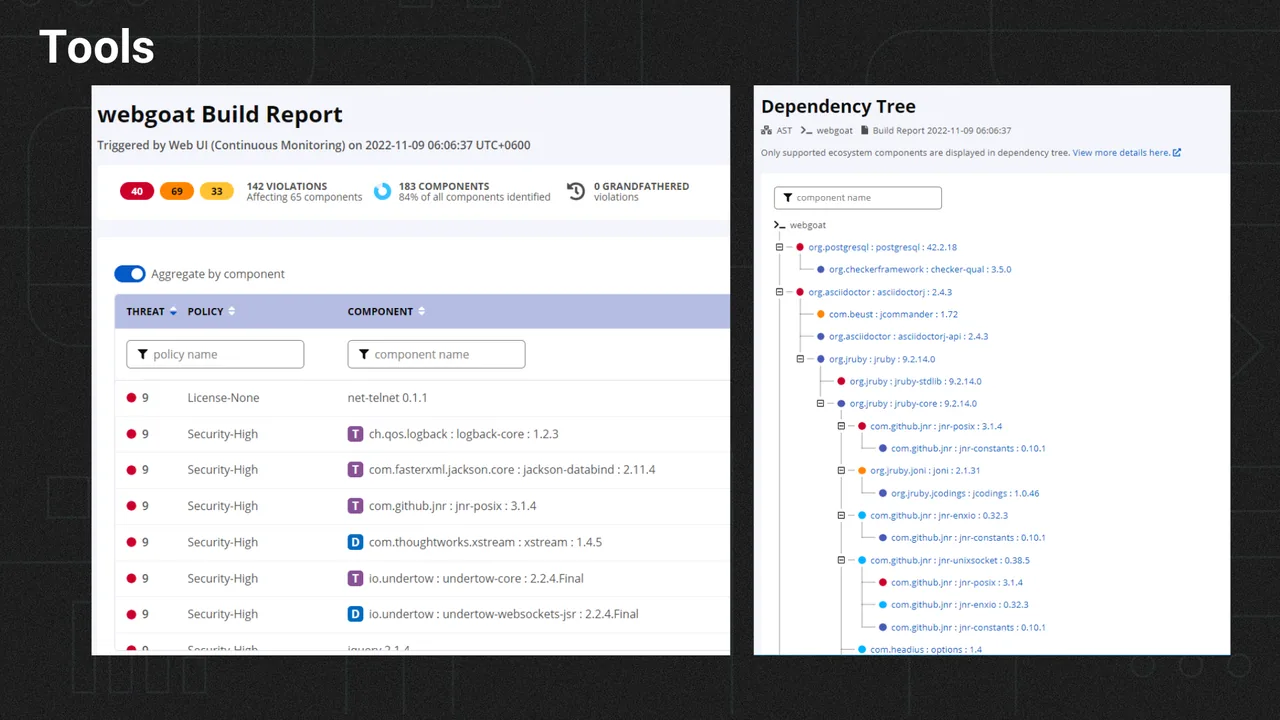
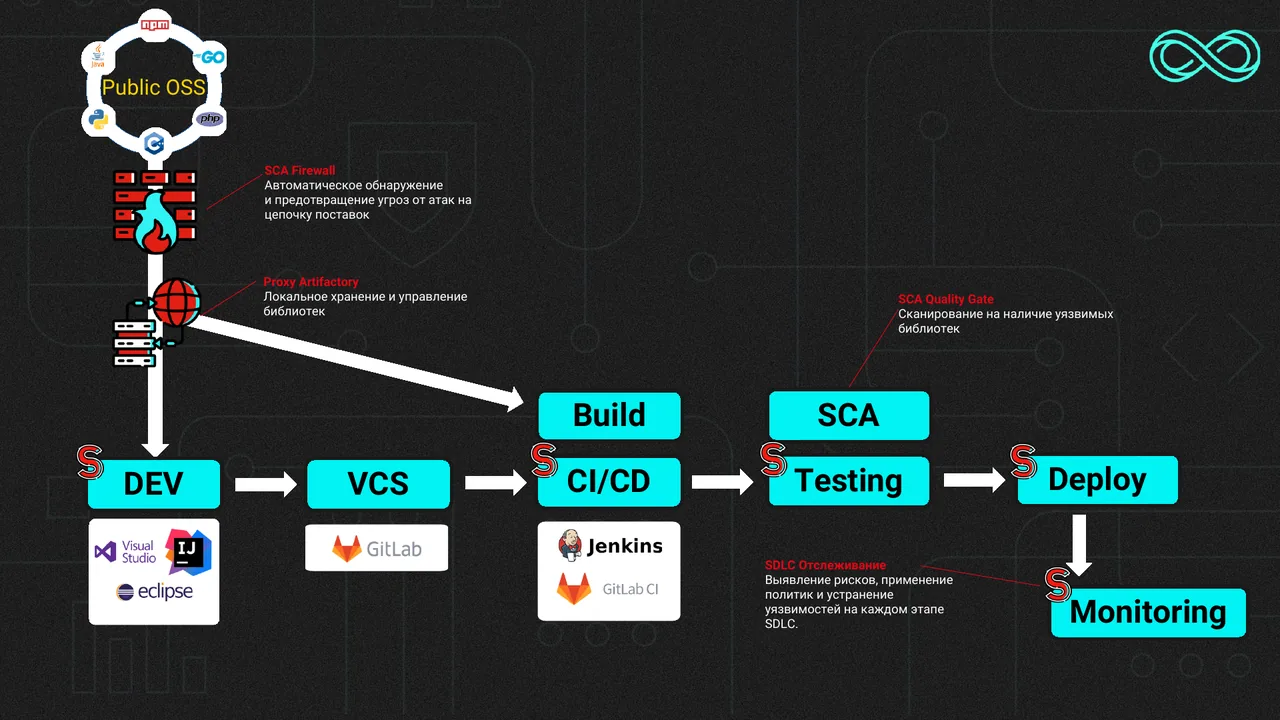
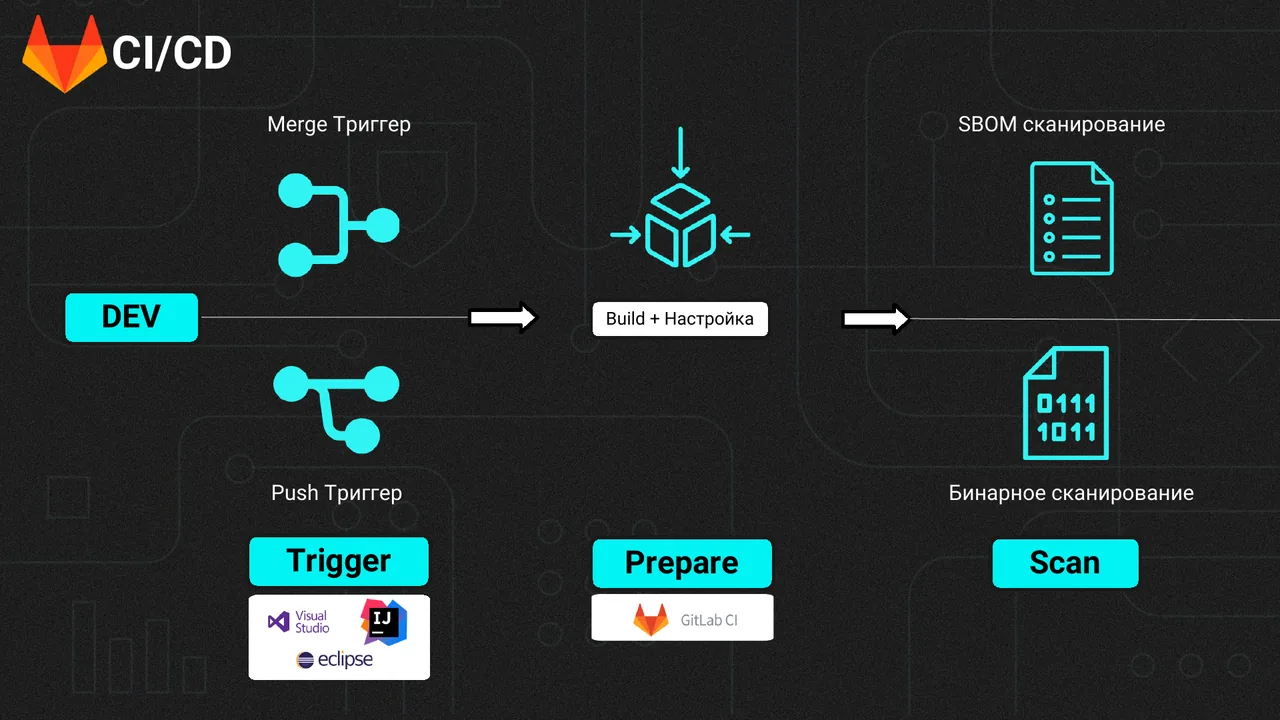
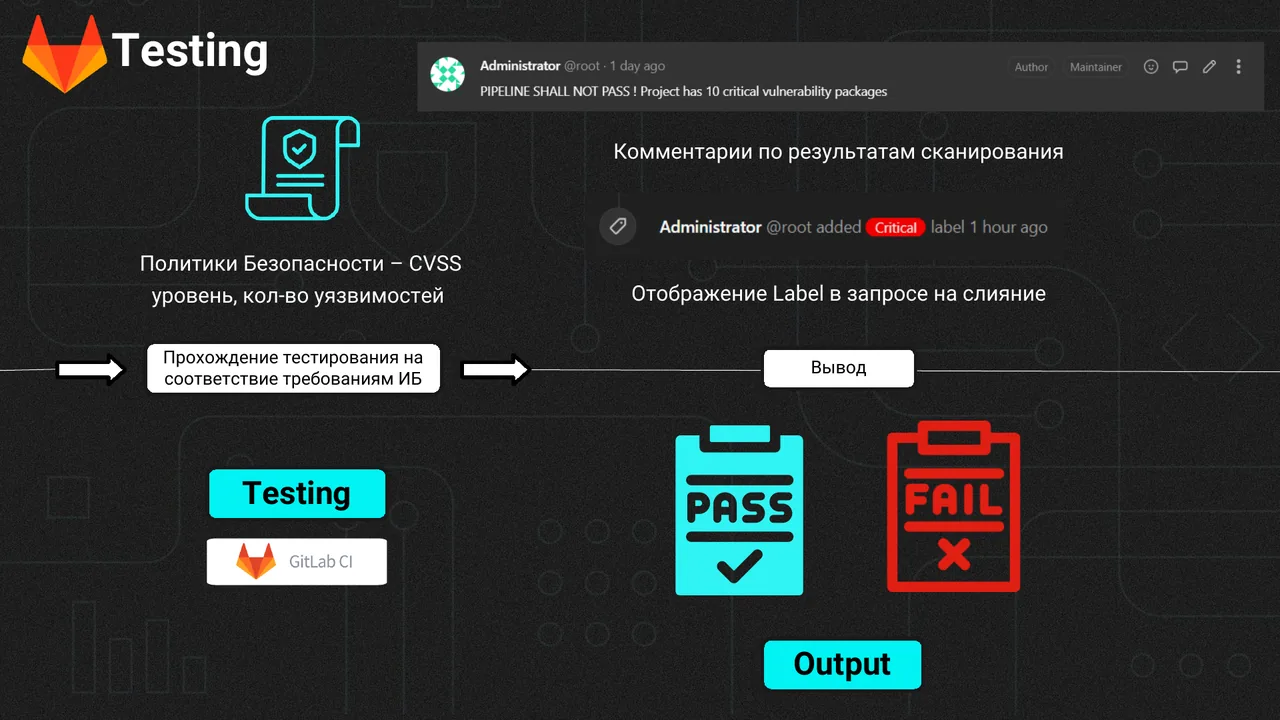
How SCA works: direct and transitive dependencies, SBOM, firewall, pipeline check and audit; the criteria for choosing open-source components.
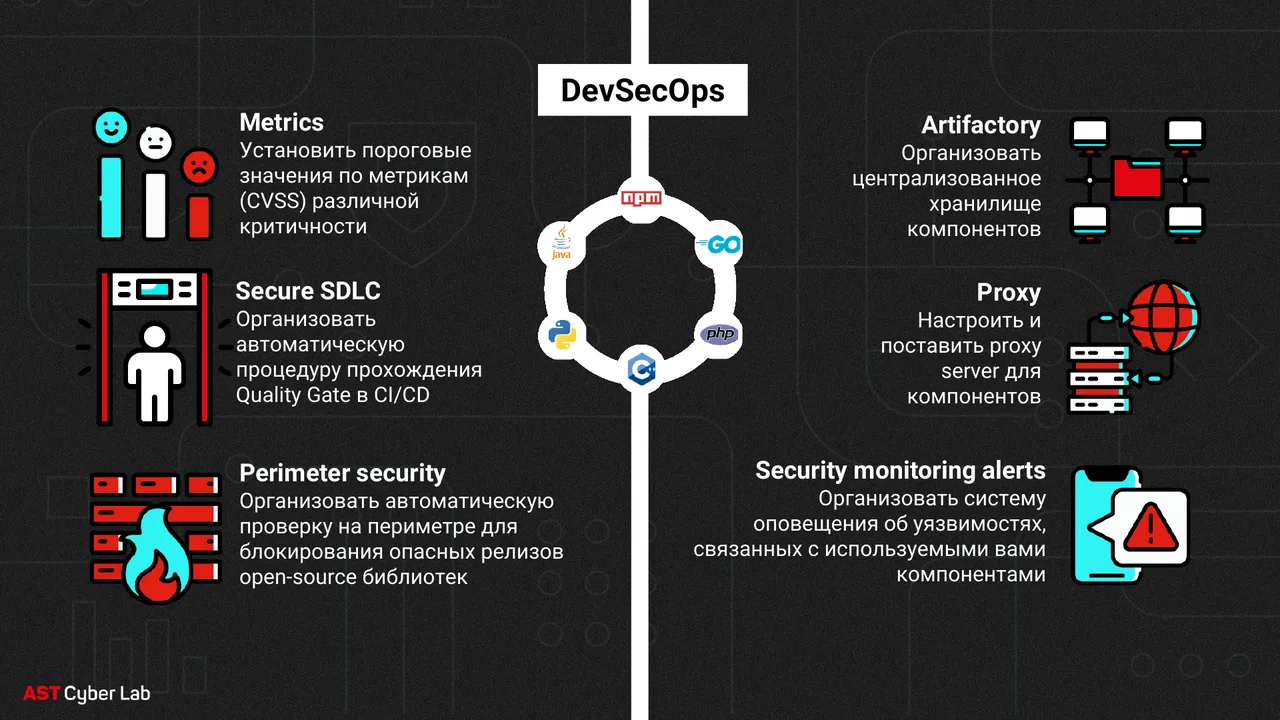
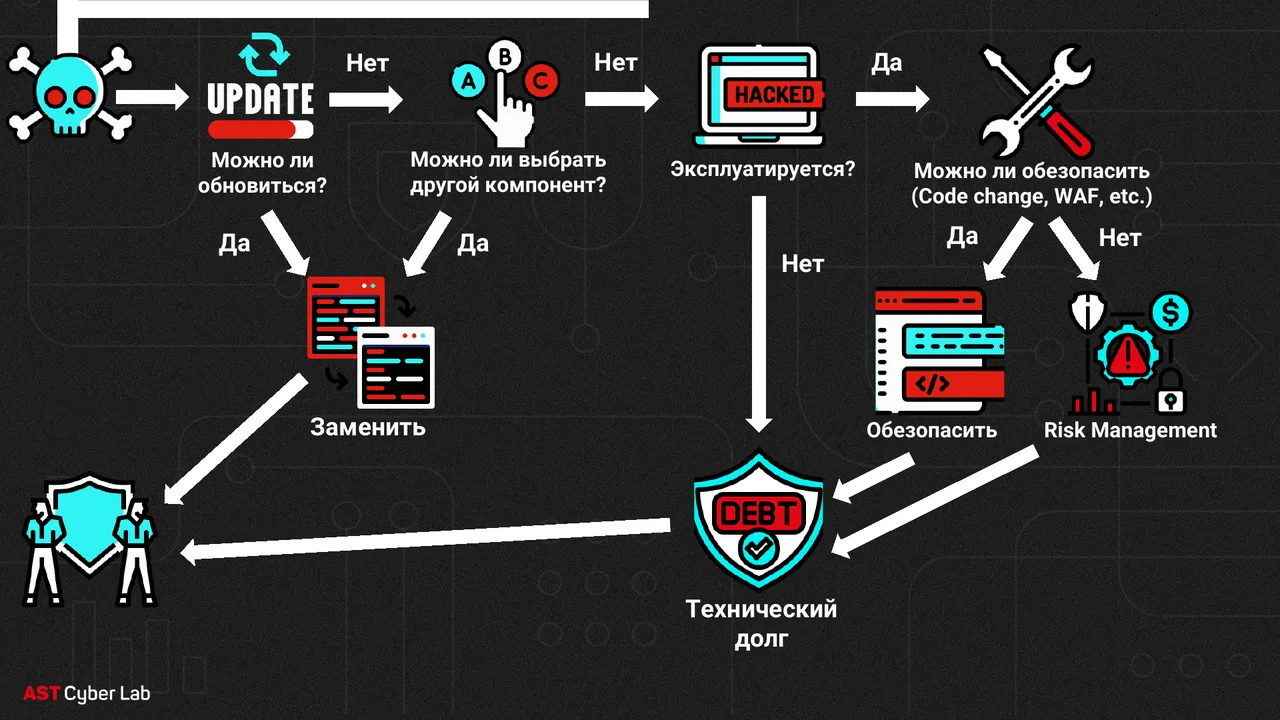
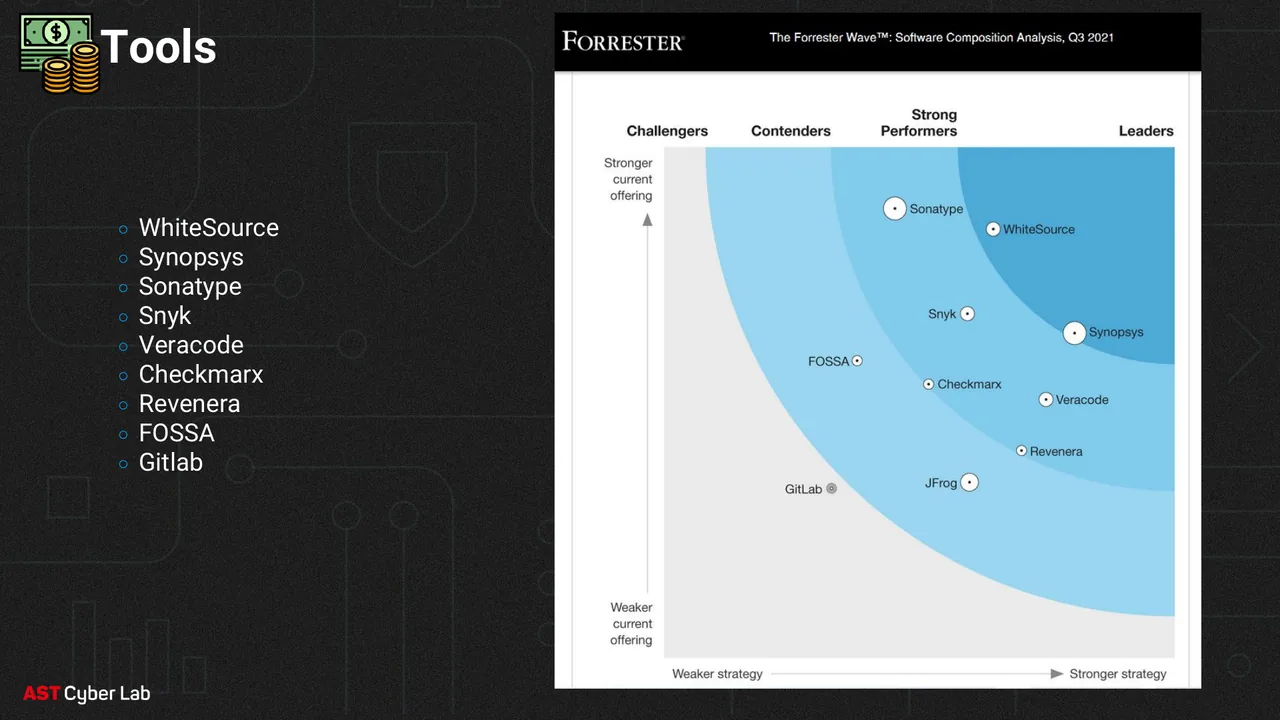
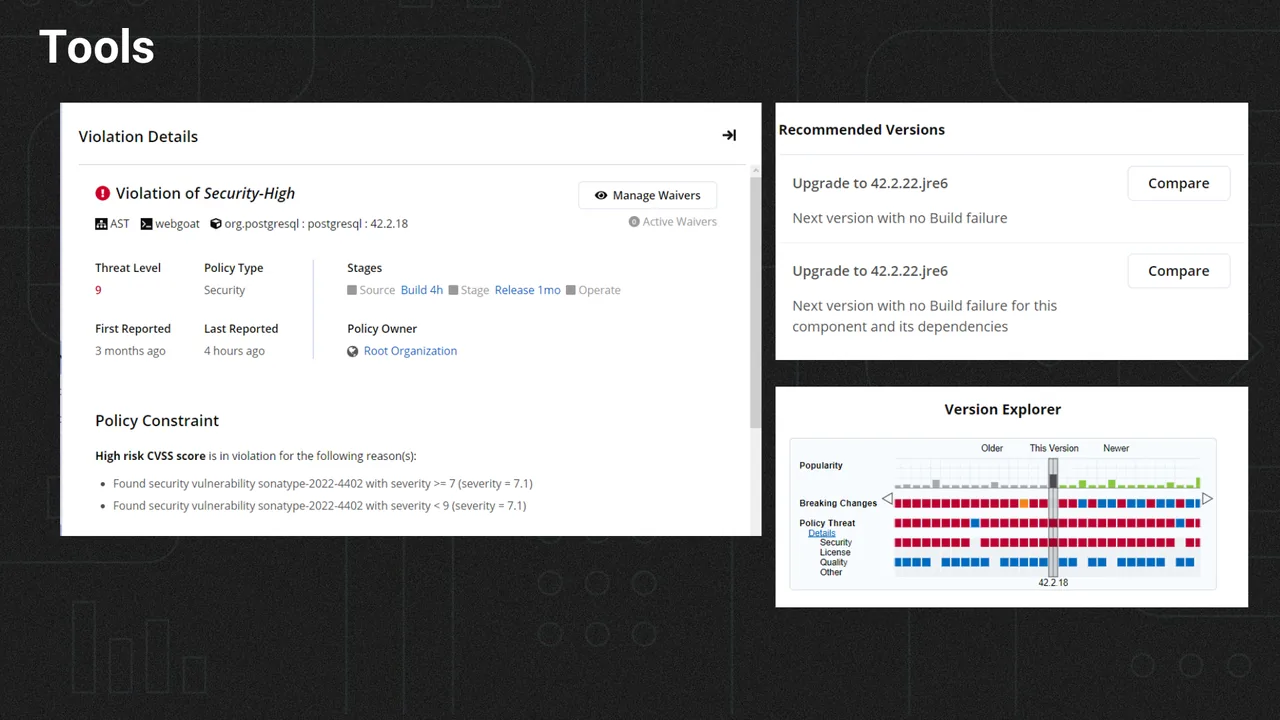
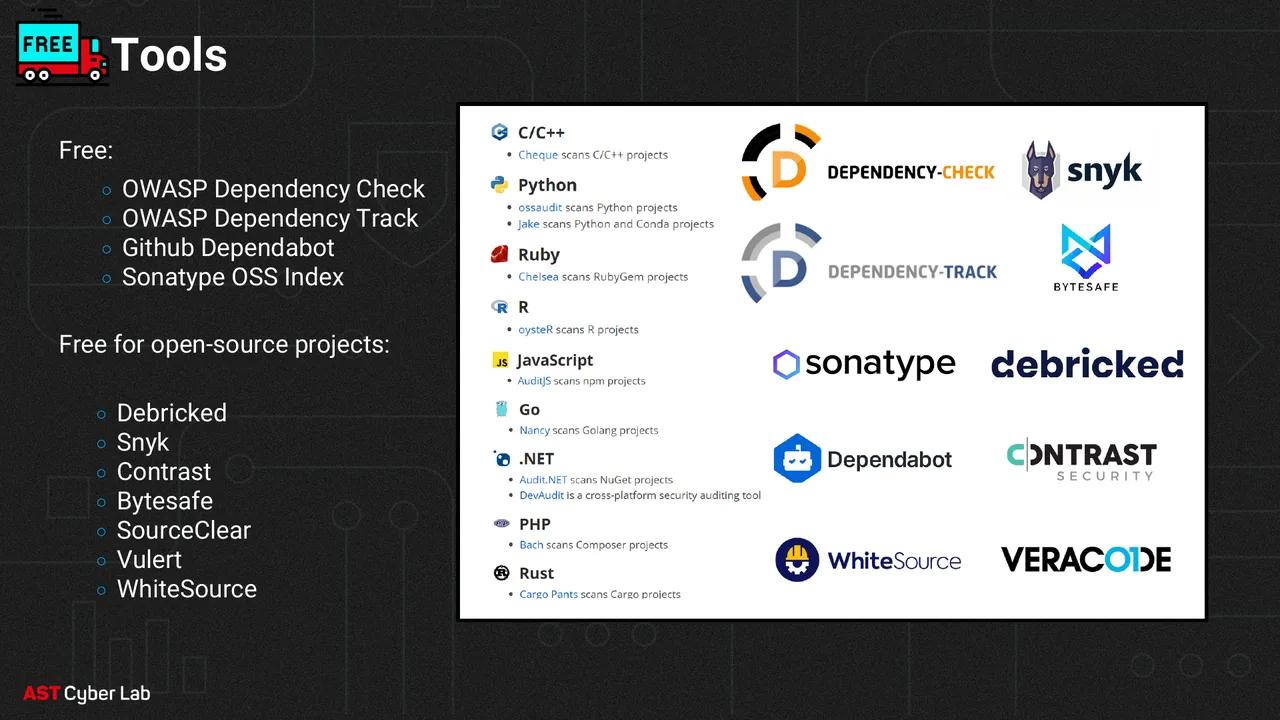
The DevSecOps process: metrics, proxy repository, Quality Gate in CI/CD, alerts, a scheme for fixing a vulnerable library, and an overview of free and commercial tools.