Digital Farabi 2026 International Forum · Almaty · 17 April 2026
AppSec & DevSecOps 101: security in the AI era
An introductory talk at the forum "Digitalization and Artificial Intelligence as a Strategic Vector of the Future": what AppSec and DevSecOps are, which technologies cover them and how AI changes development security.
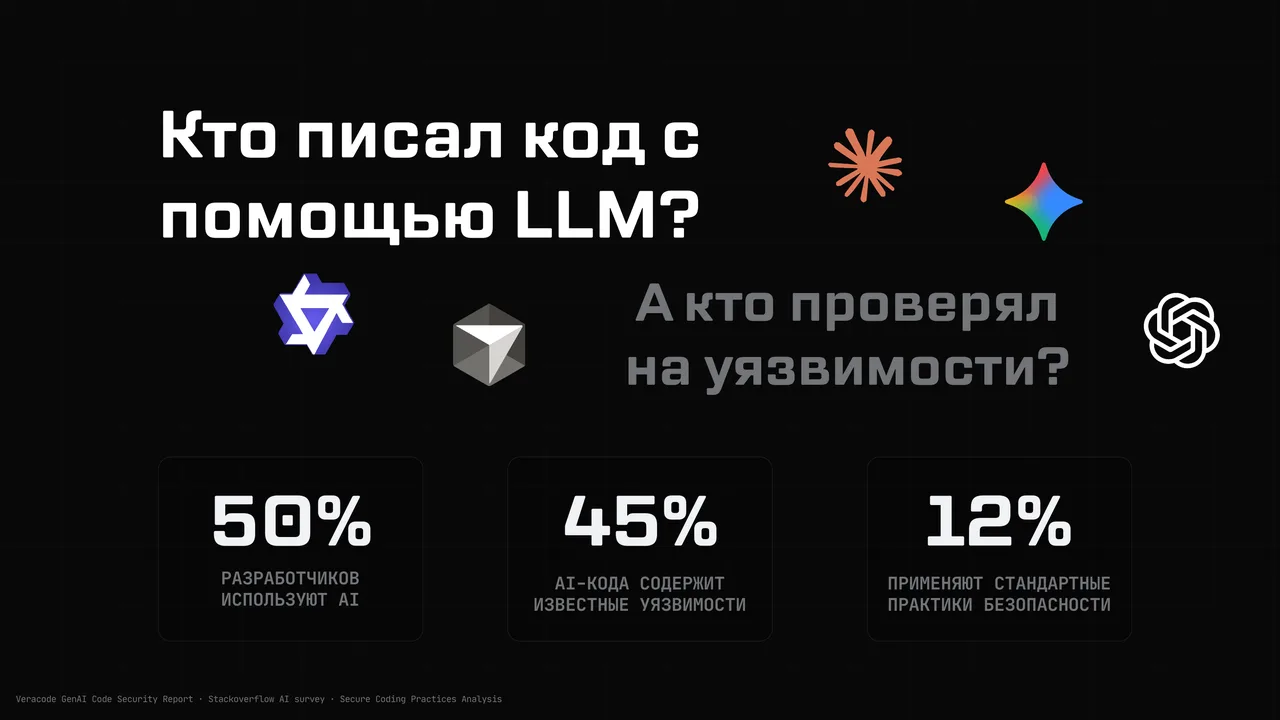
Half of developers already write code with AI, and a noticeable share of AI code contains known vulnerabilities, and only a few check it.
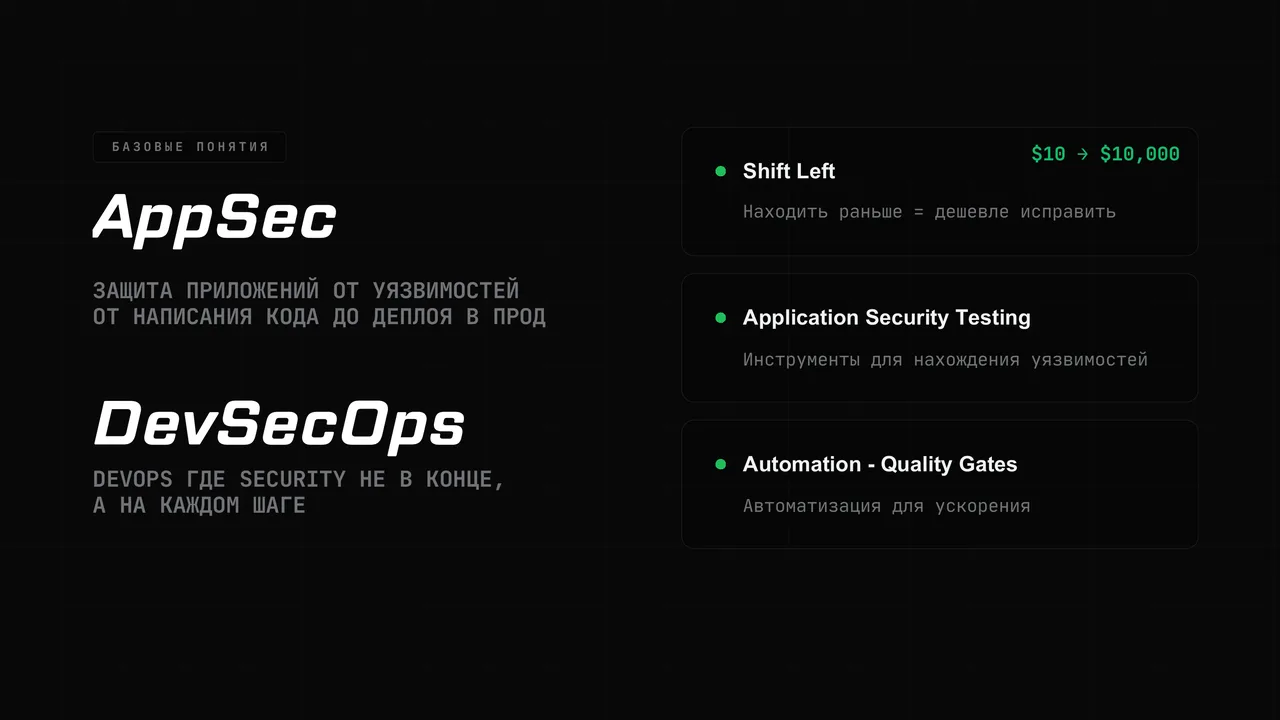
Basic concepts: AppSec is protecting applications from writing code to production, DevSecOps is security at every step, not at the end. Shift Left: the earlier you find it, the cheaper it is to fix.
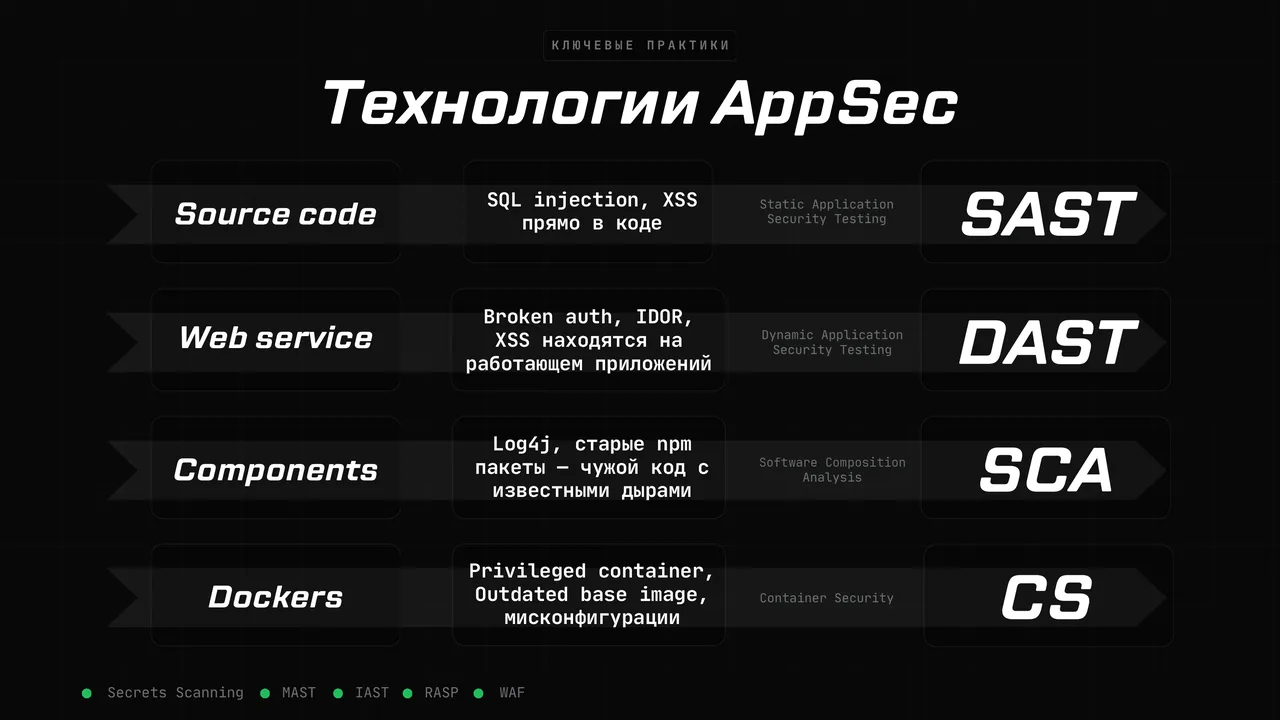
Technologies: SAST for source code, DAST for the running application, SCA for third-party libraries, Container Security for images, plus secret detection, MAST, IAST, RASP and WAF.
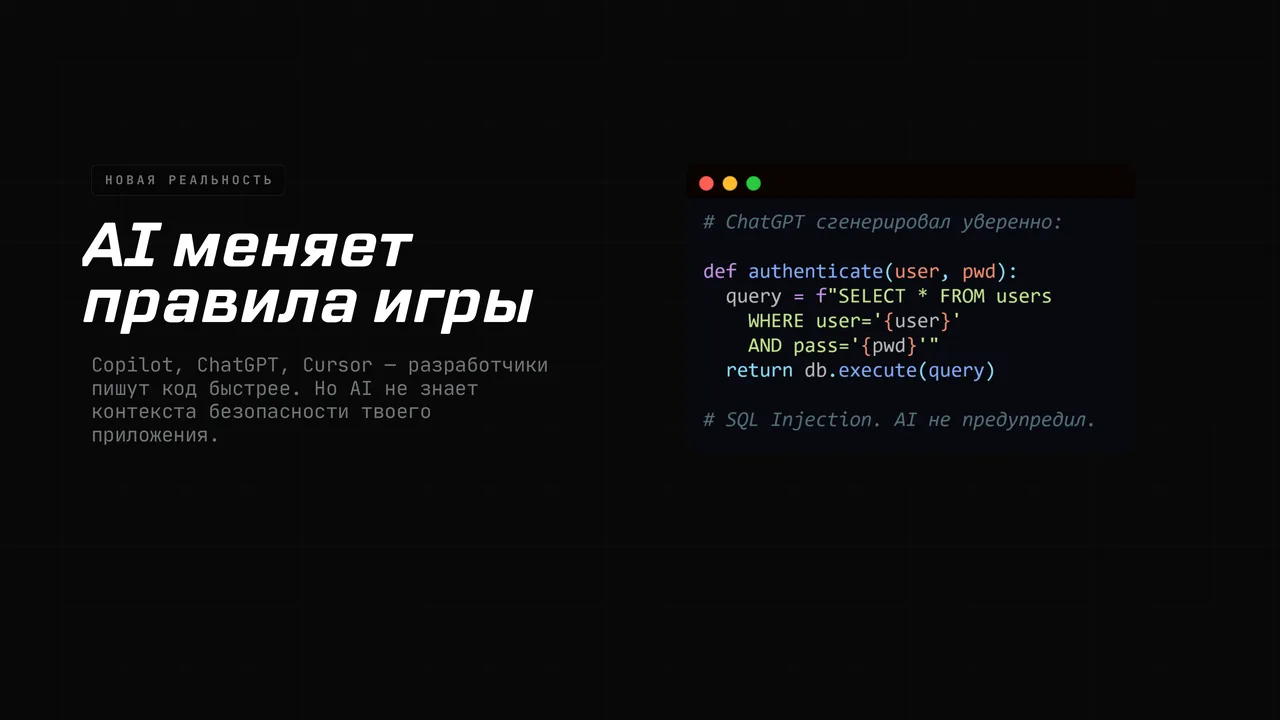
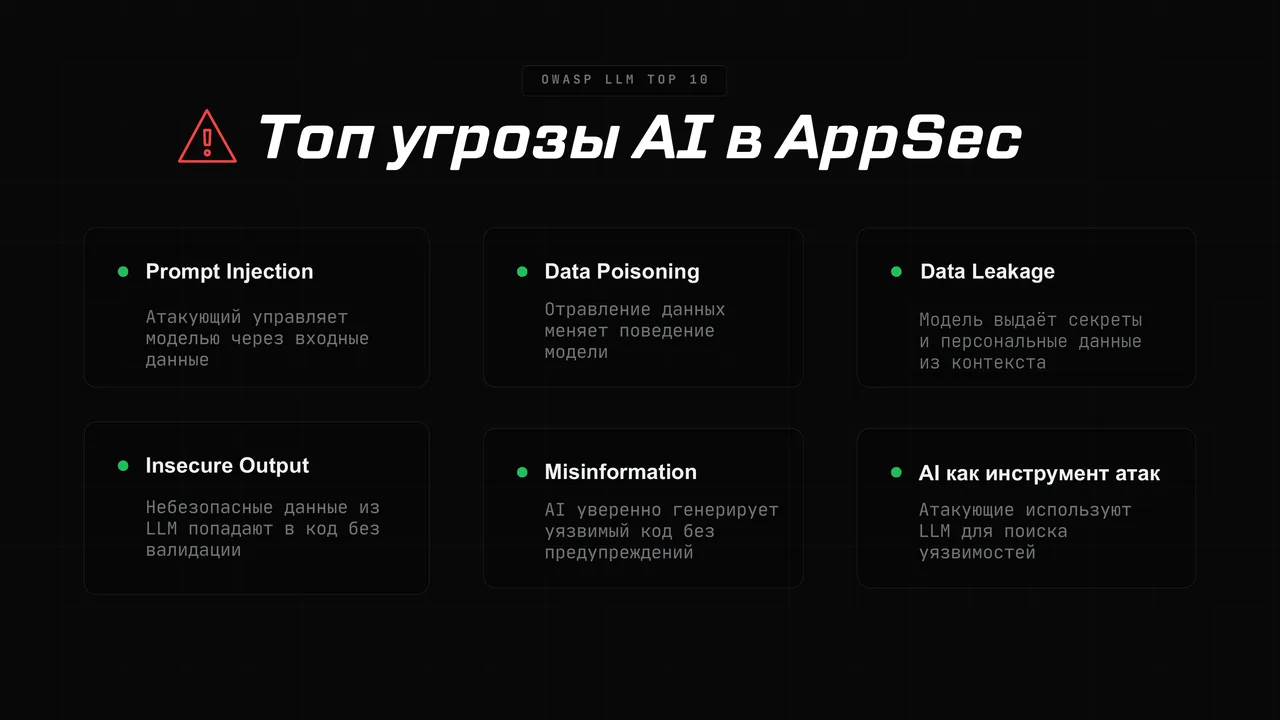
The new reality: AI writes code faster but does not know the security context. The main threats from the OWASP LLM Top 10 are prompt injection, data poisoning, data leakage, unsafe output, misinformation.
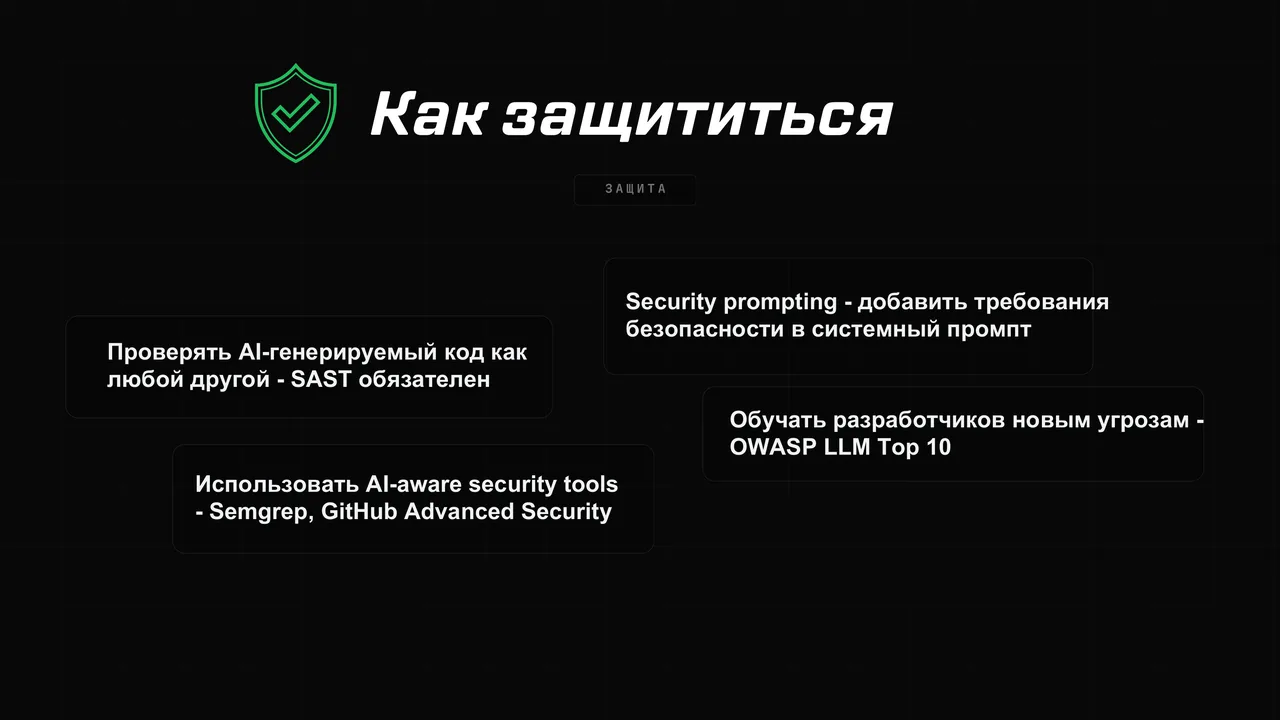
How to defend: security requirements in the system prompt, SAST for AI code like for any other, training developers on new threats.
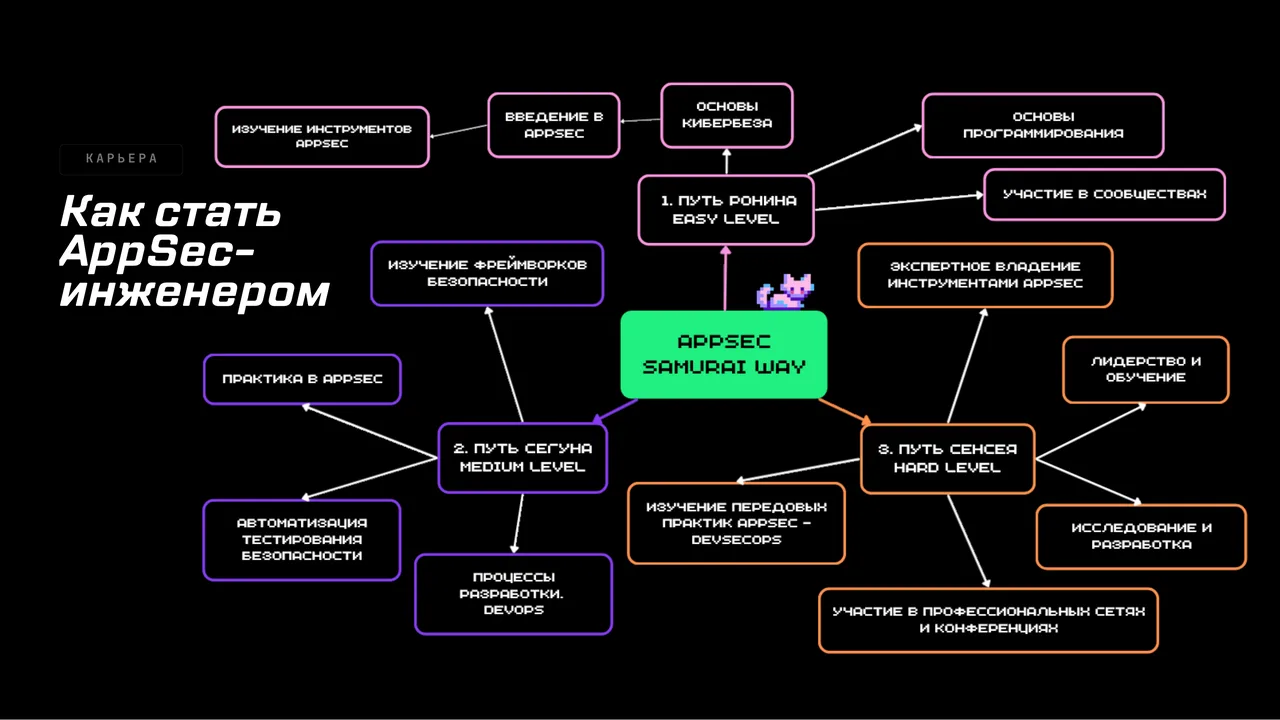
Career: how to become an AppSec engineer and why now: the field is growing fast and there are not enough specialists.