KazHackStan 2025 · Secure Development Day · Almaty · 17–19 September 2025
A gamified guidebook on secure development: how to build AppSec without millions of dollars
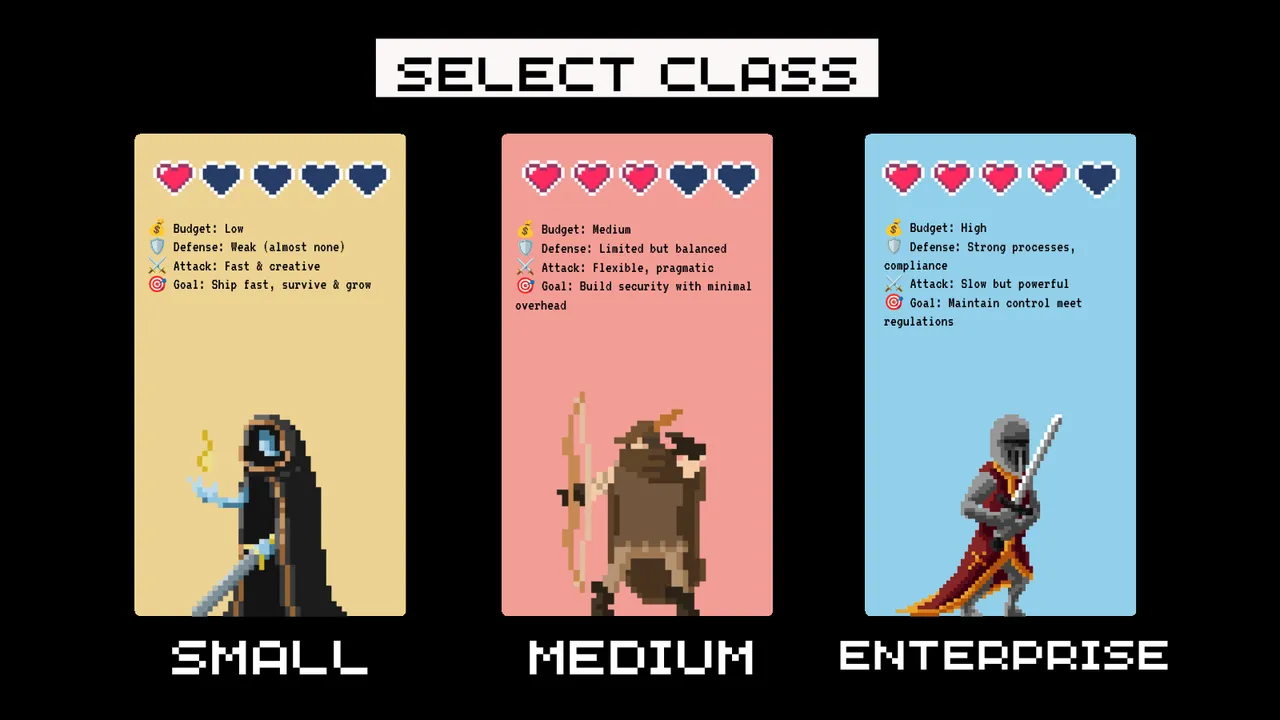
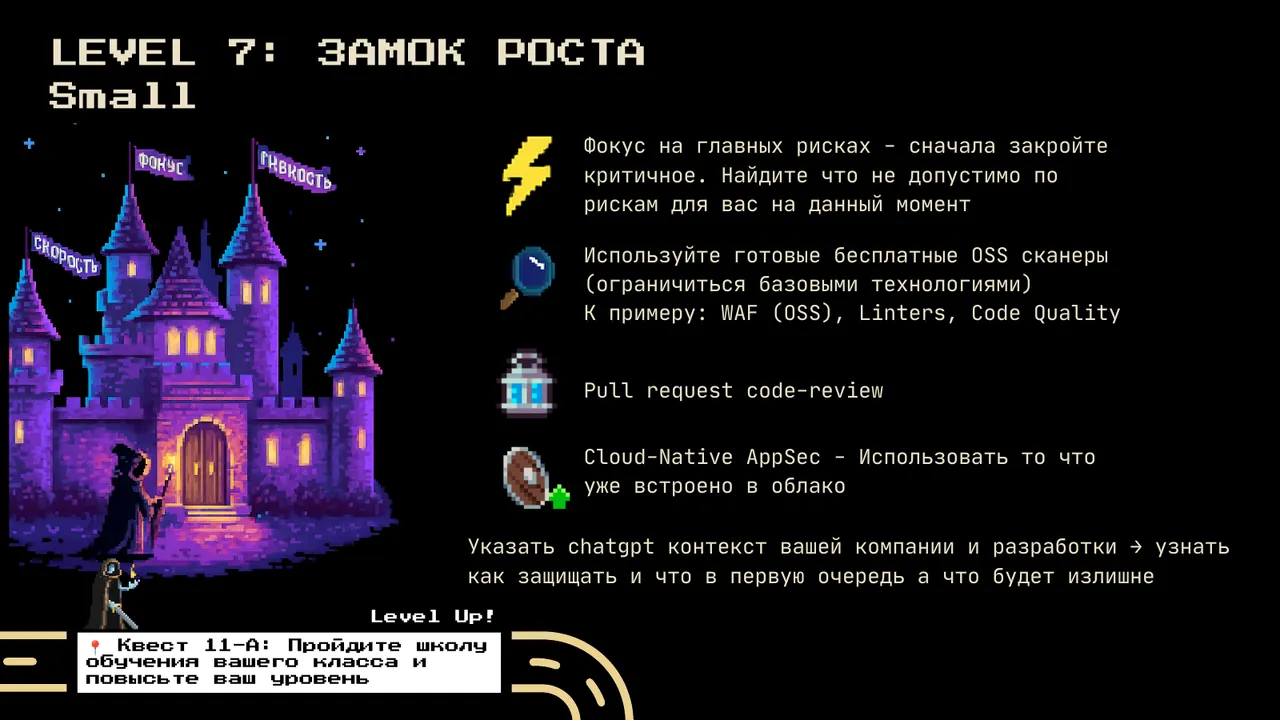
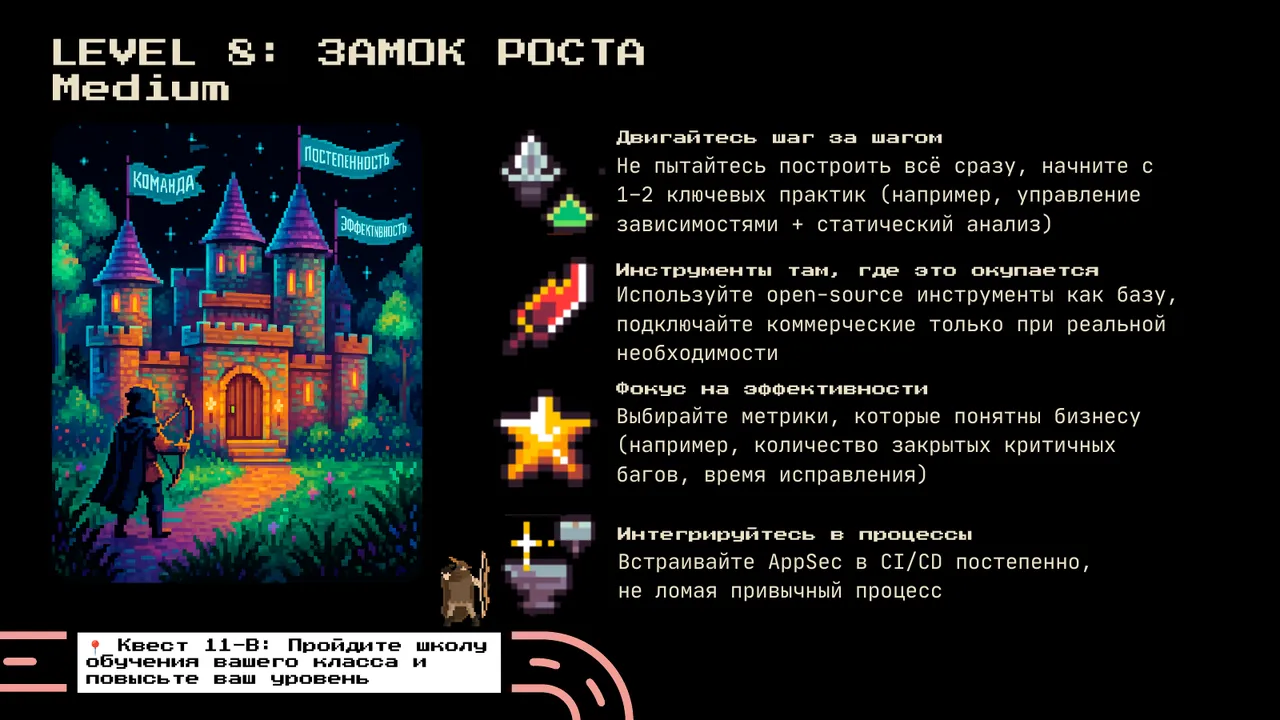
AppSec as a game: you choose a company class (Small, Medium or Enterprise) and pass levels from the first "why do we need security" questions to a security review with champions.
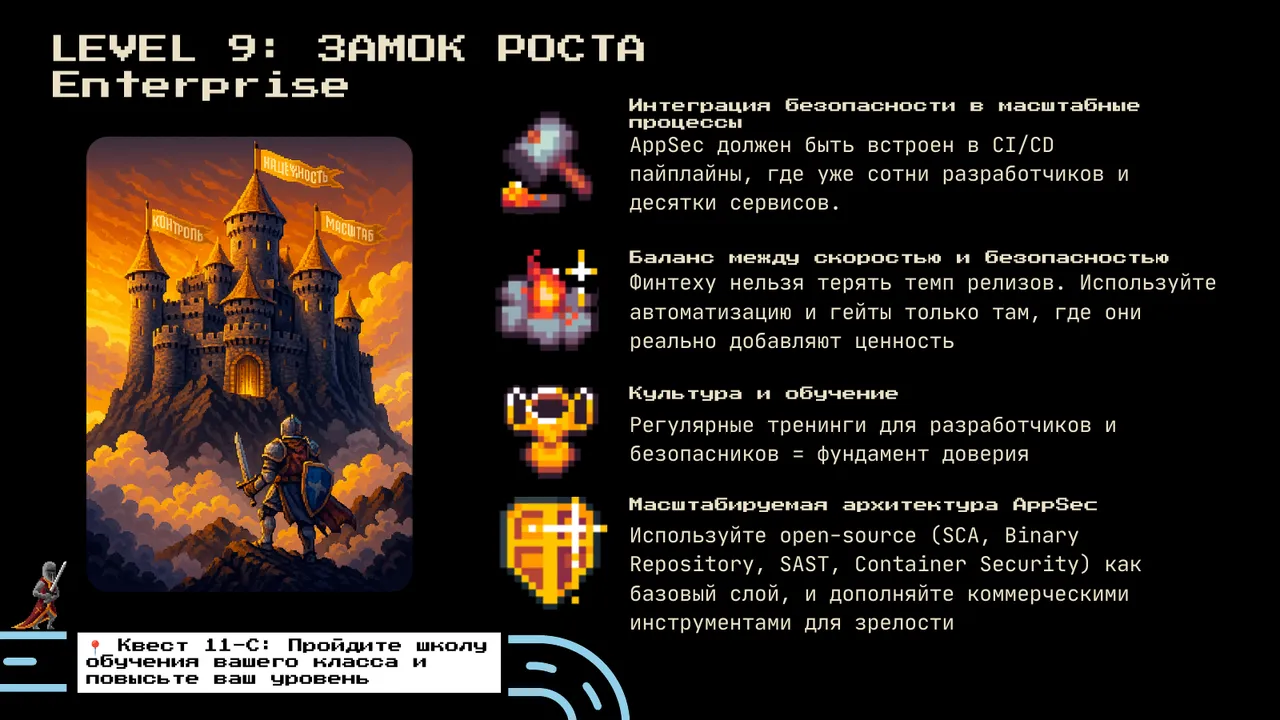
Three company classes with different budgets and goals: a small team needs to survive and grow, a medium business needs minimal overhead, a large company needs control and regulatory compliance.
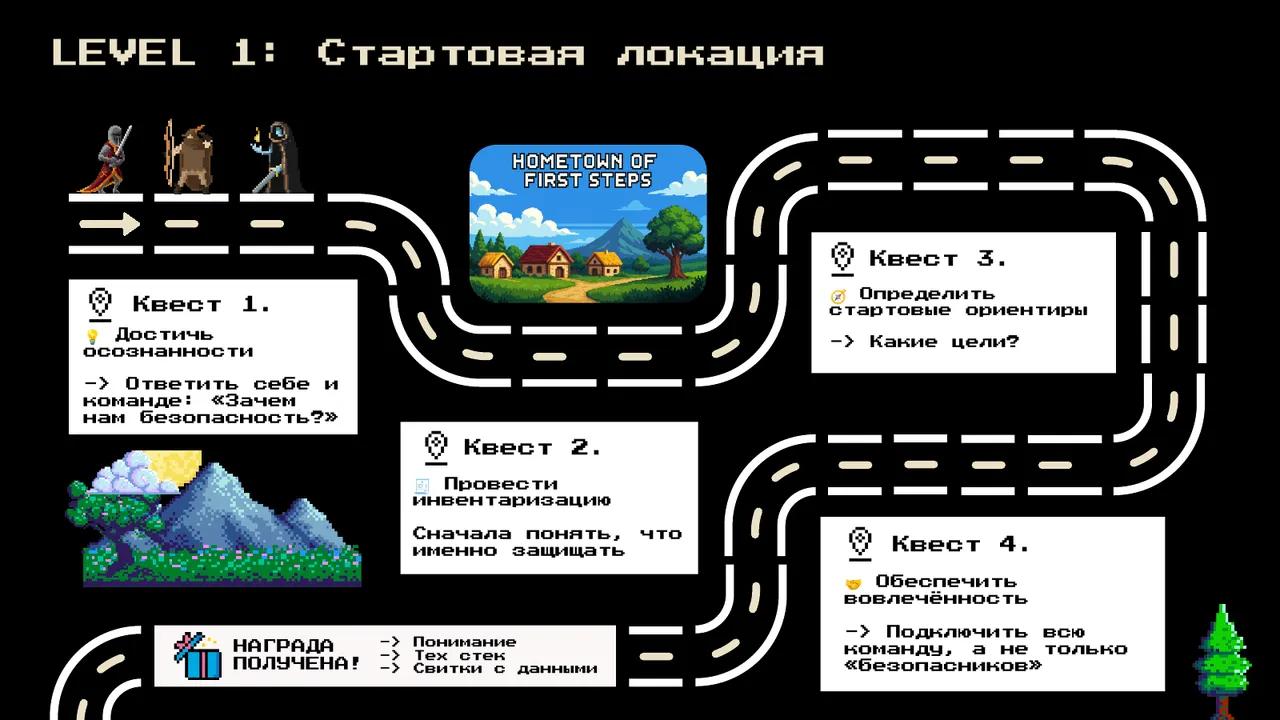
Start: answer for yourself why security is needed, take an inventory of the stack and data, define goals and involve the whole team, not only security people.
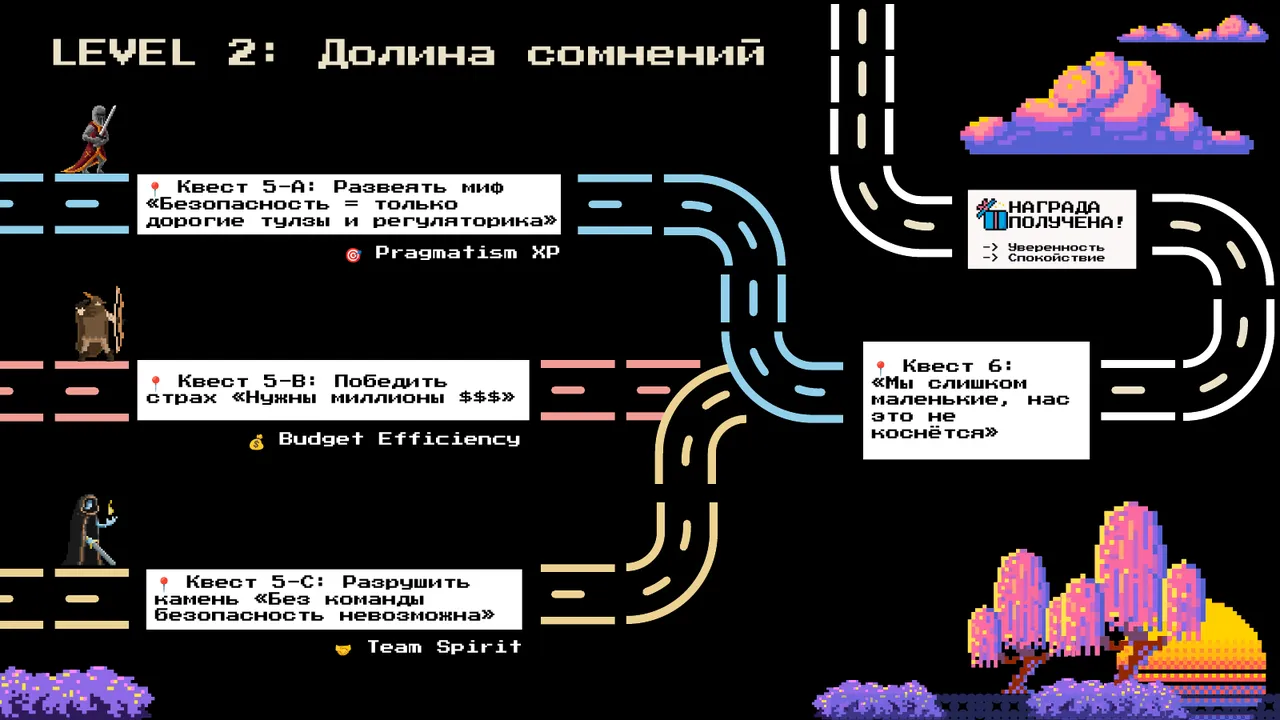
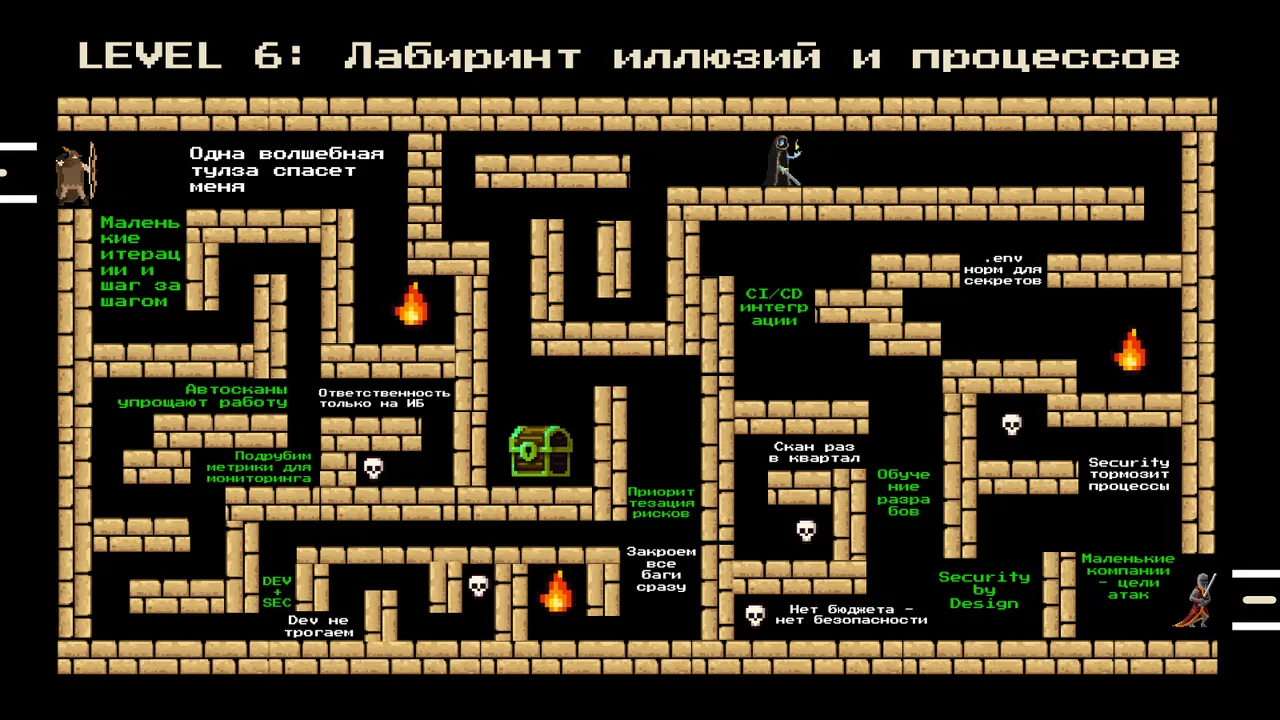
Myths that prevent starting: "millions are needed", "only expensive tools", "impossible without a separate team", "we are too small, nobody will touch us".
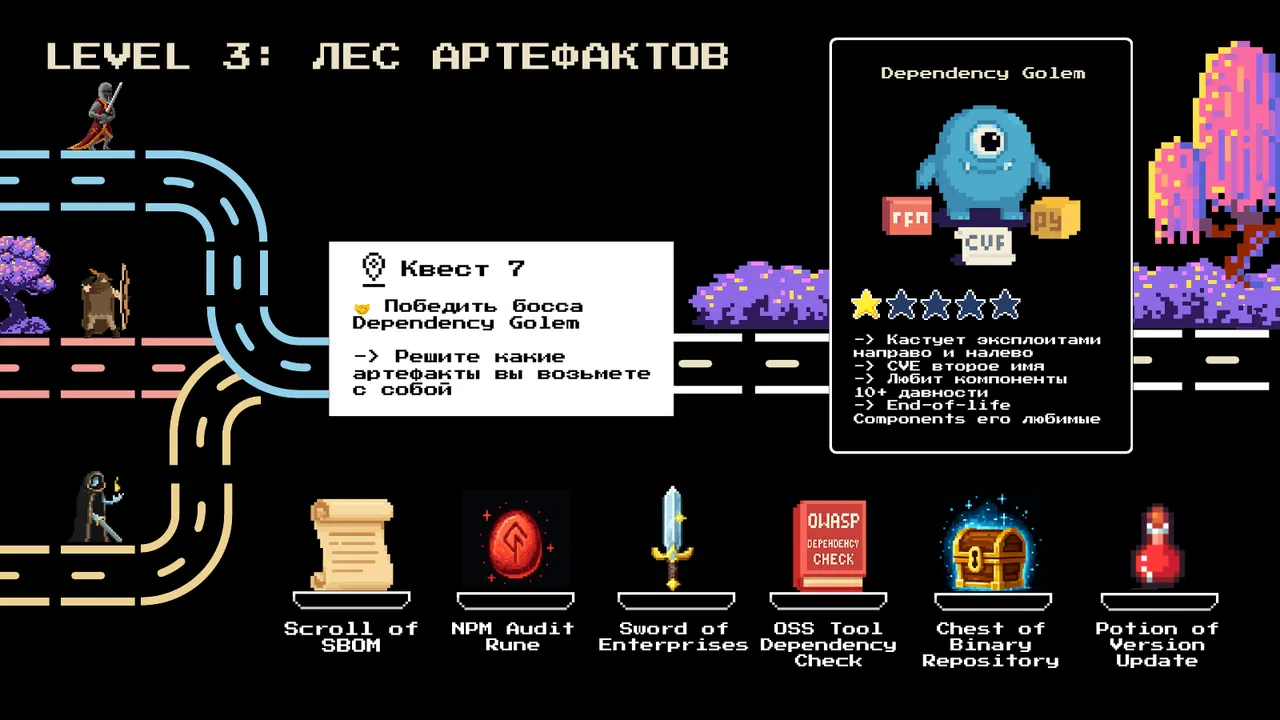
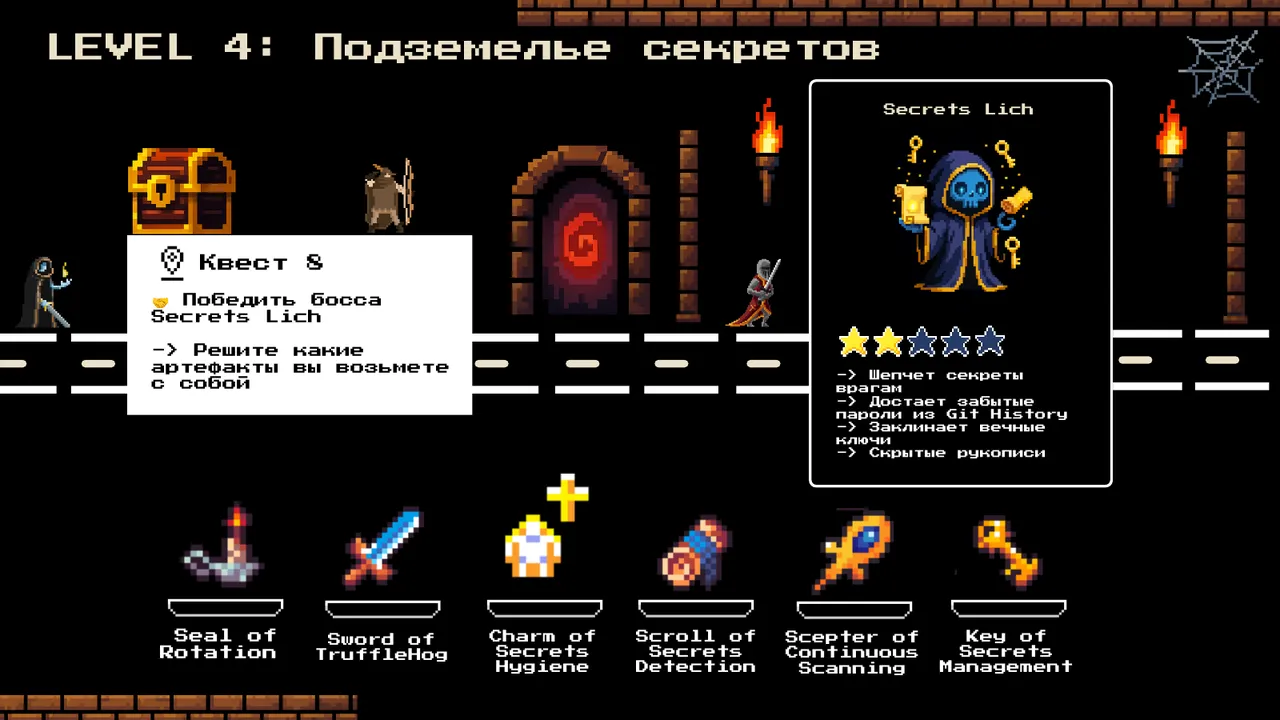
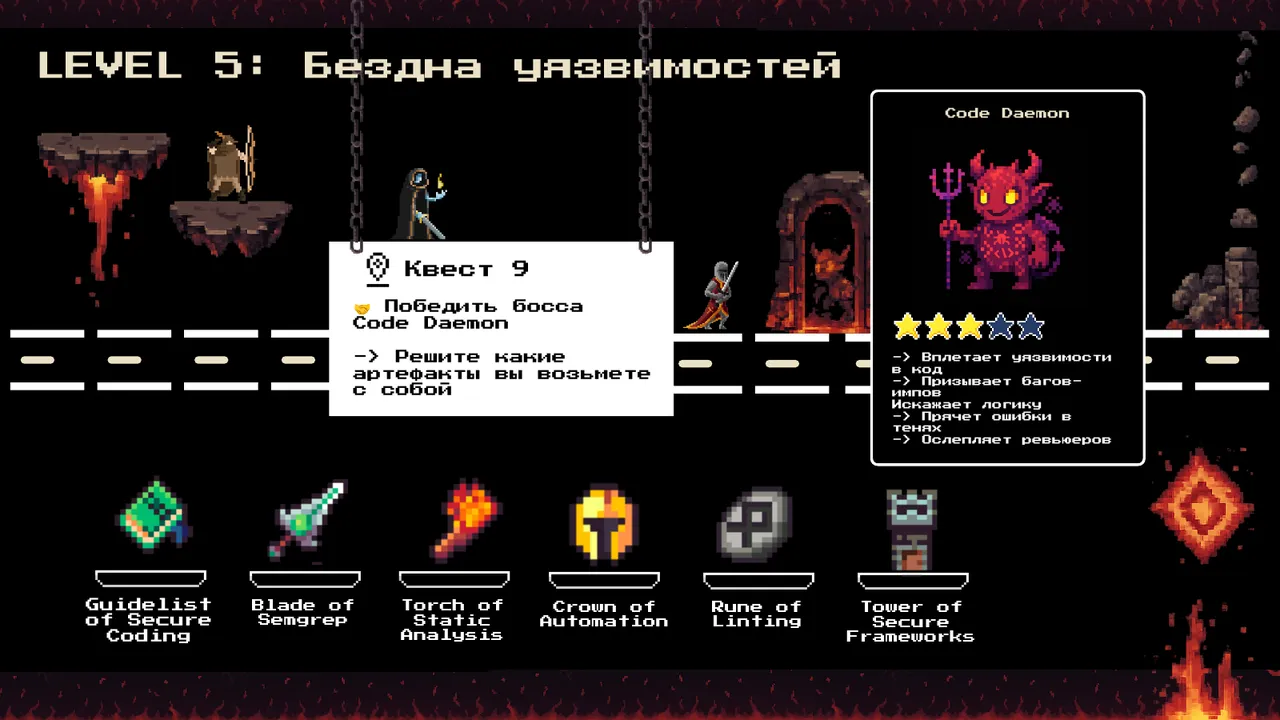
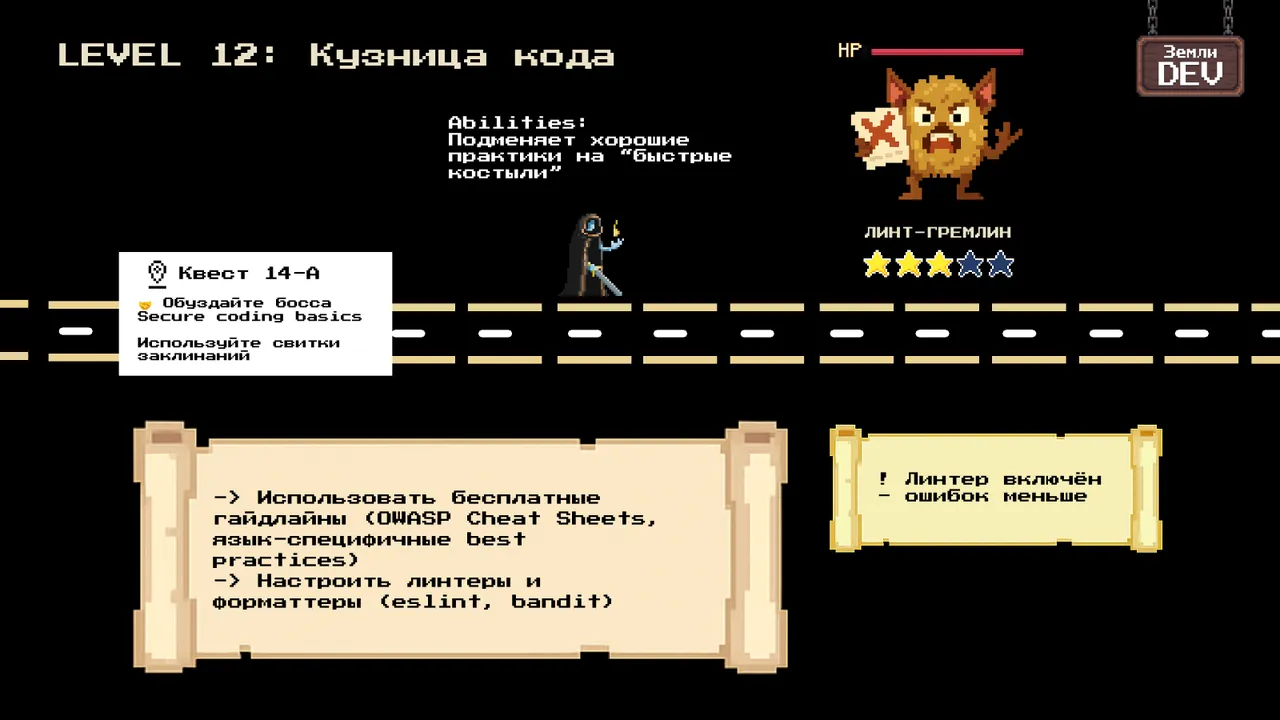
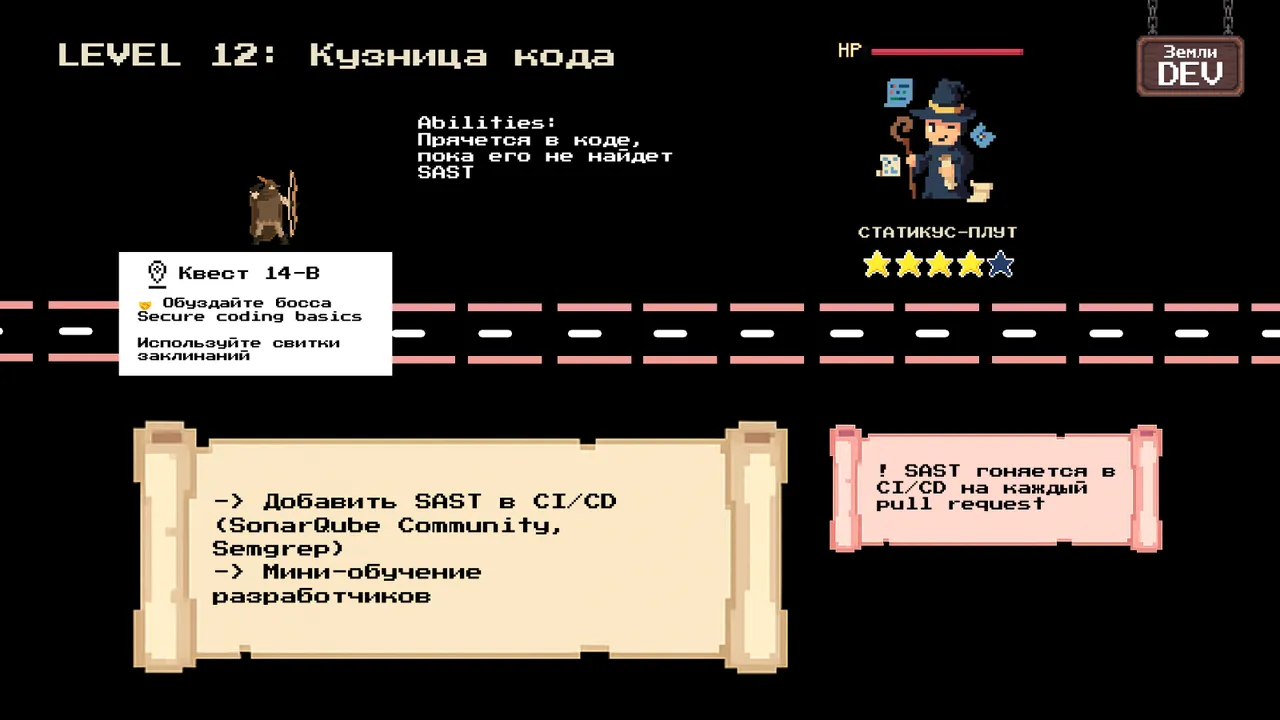
Three bosses: vulnerable dependencies (SCA, SBOM, version updates), leaked secrets (search in git history, rotation, a secrets manager) and vulnerabilities in code (Semgrep, SAST, linters).
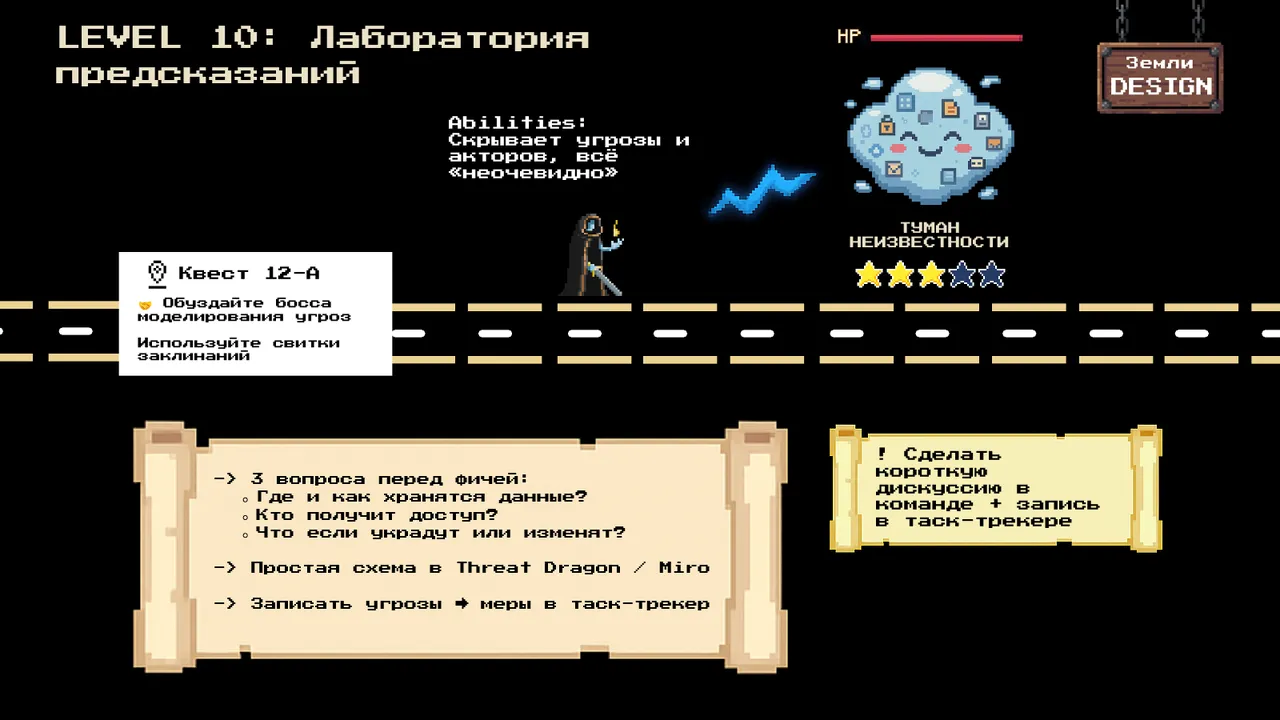
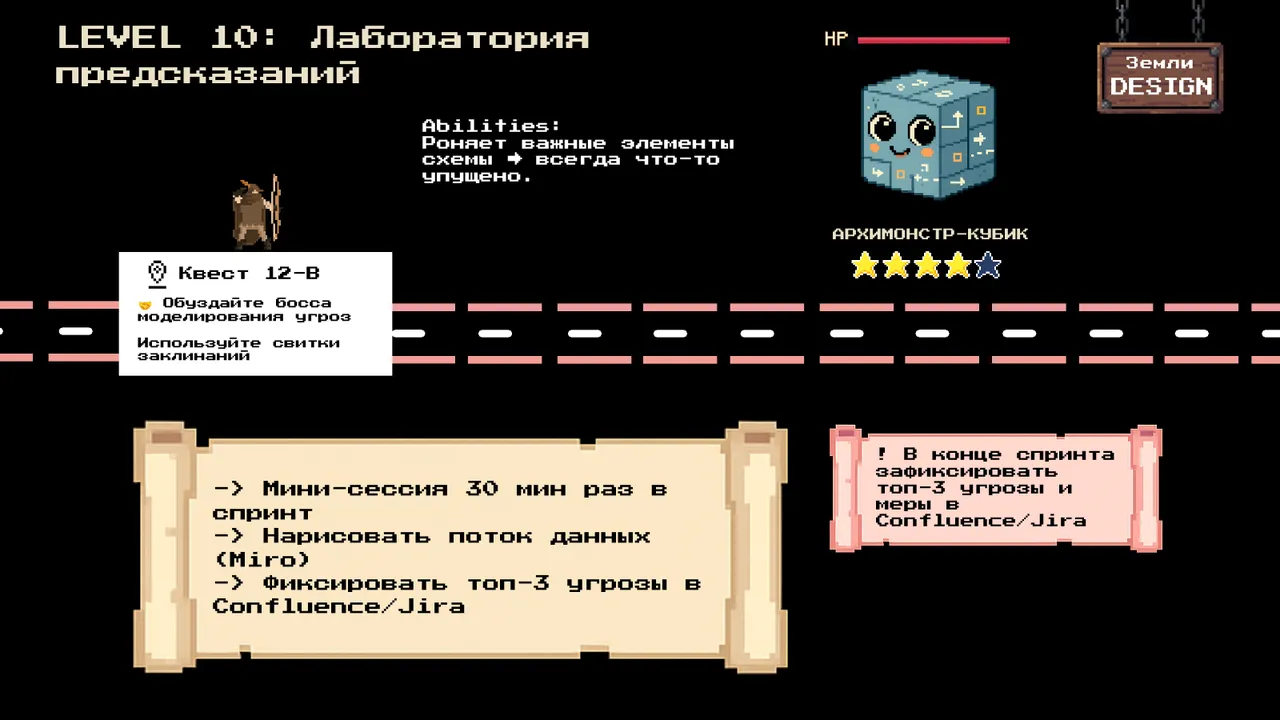
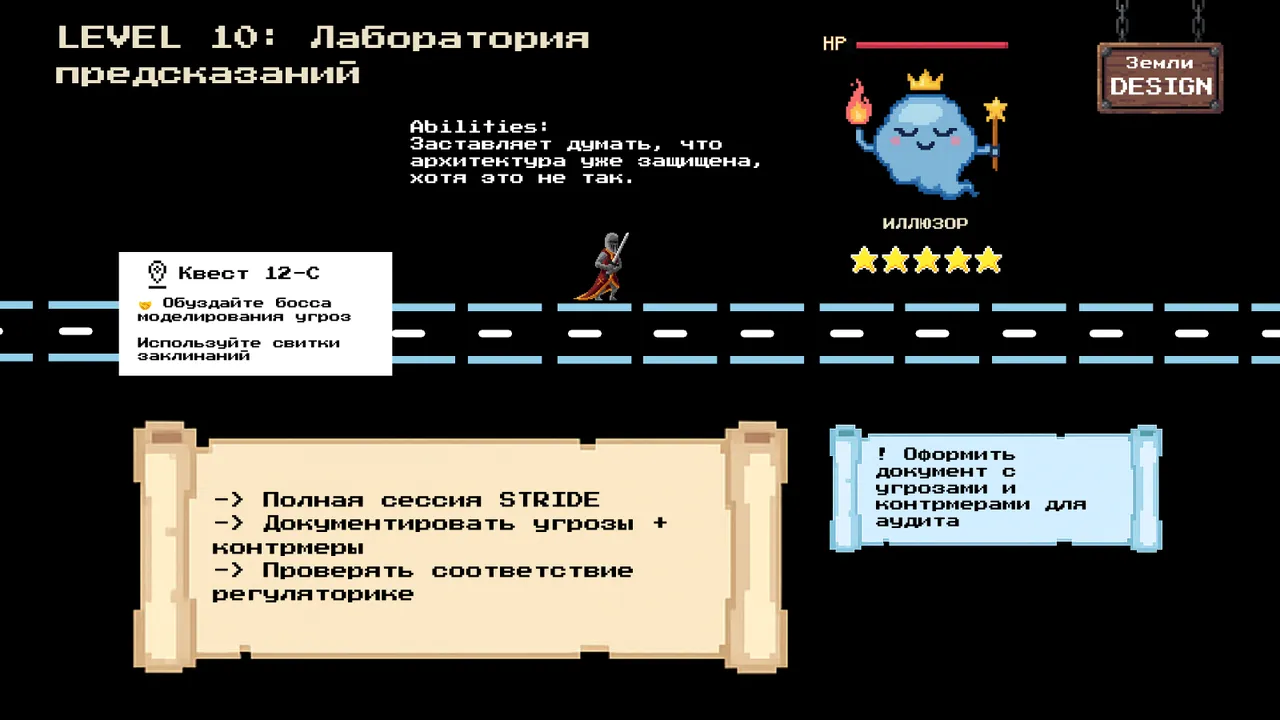
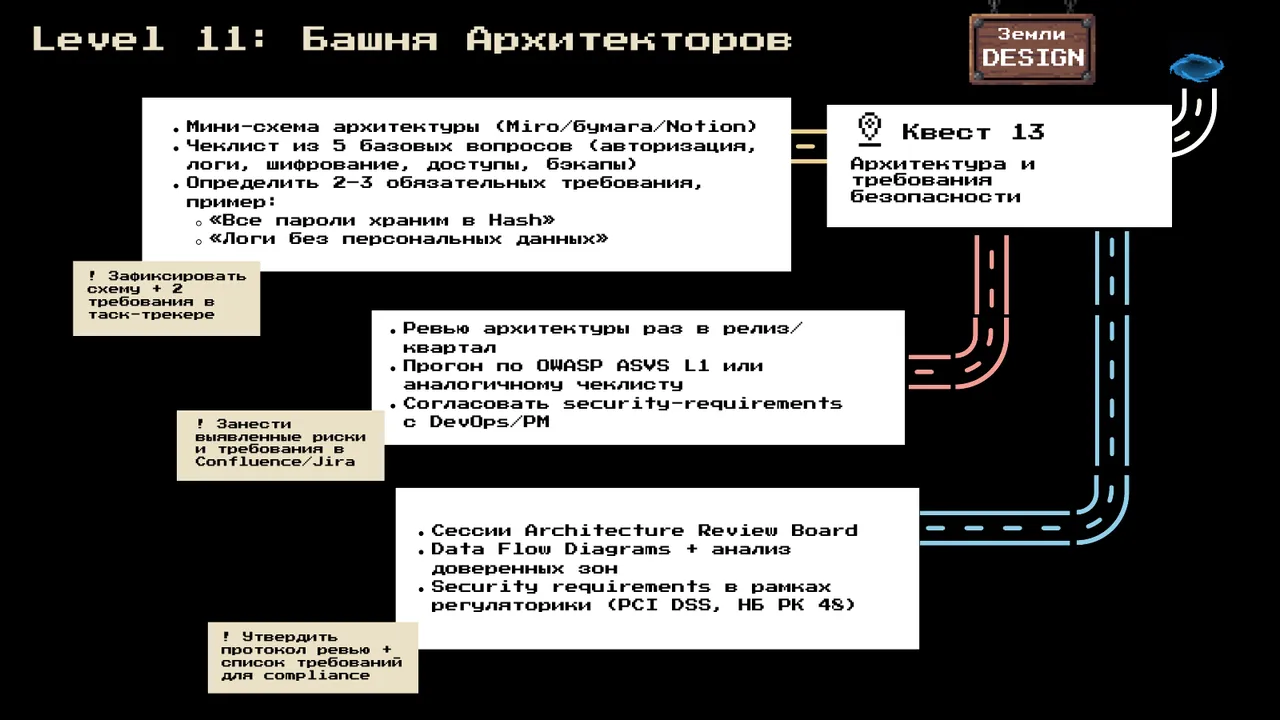
Threat modeling by levels: three questions before a feature → a 30-minute session once a sprint → a full STRIDE with a document for the audit.
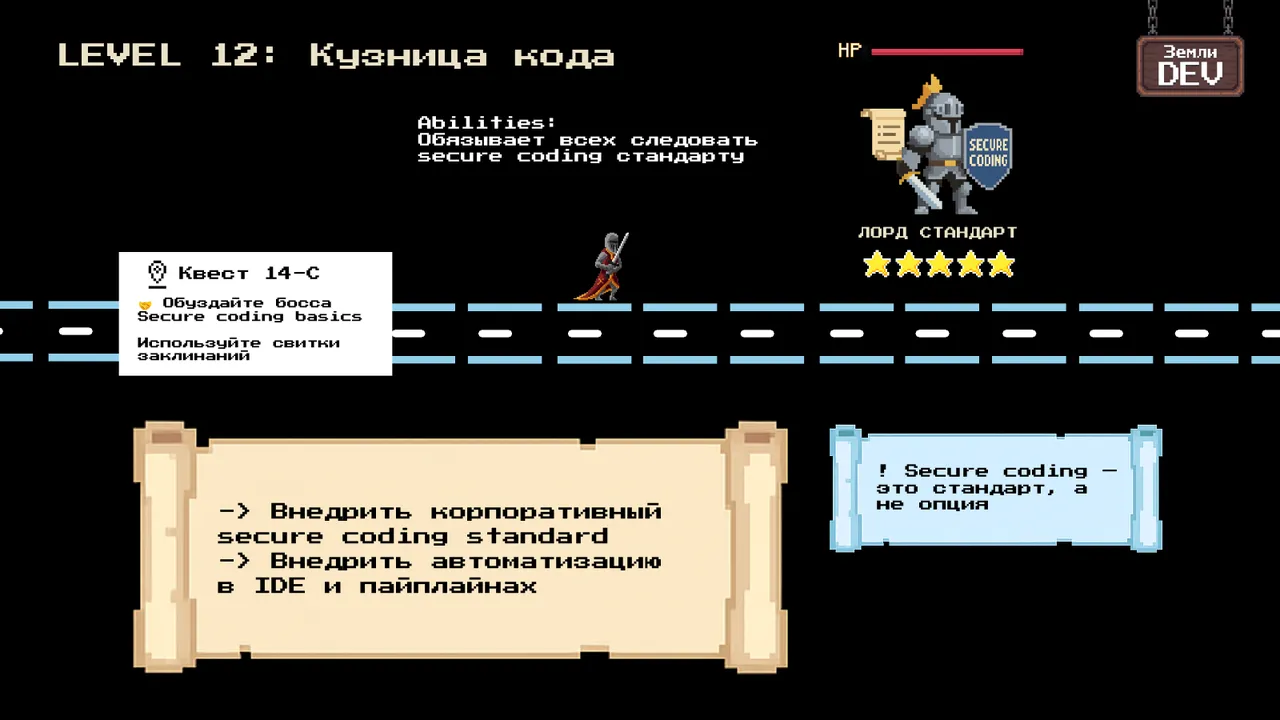
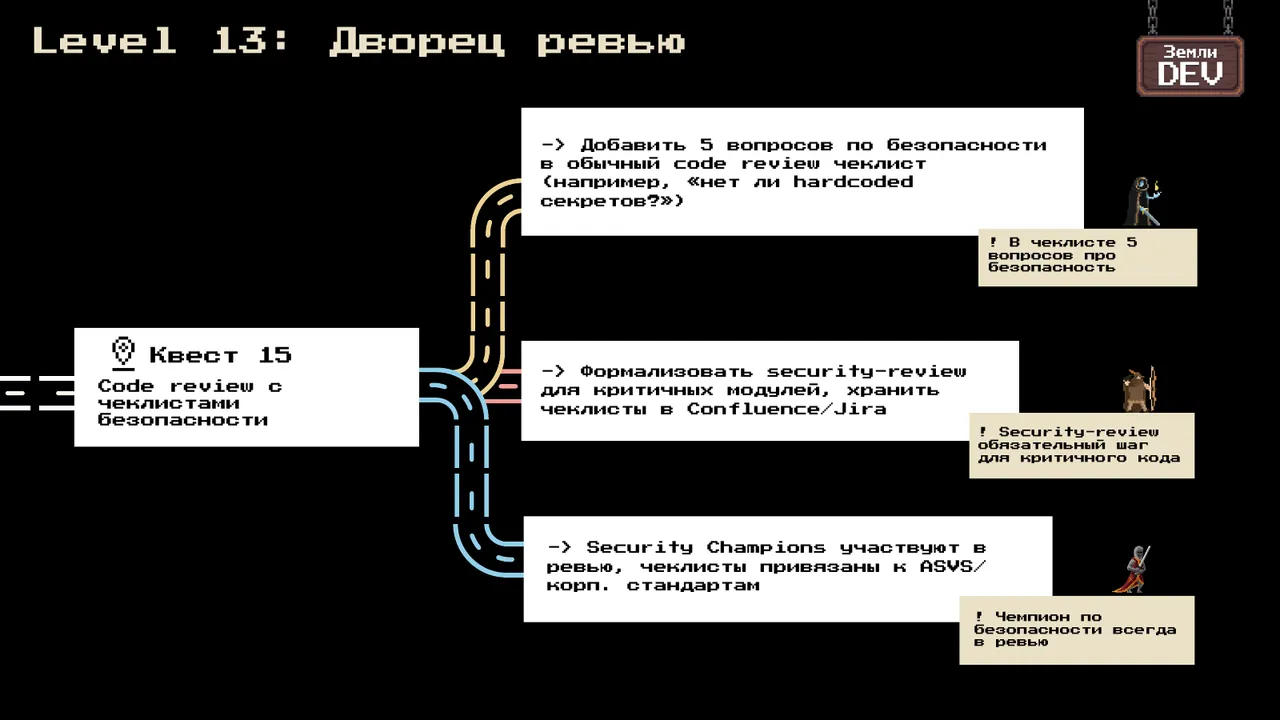
Code and review: free OWASP guidelines, SAST on every pull request, a corporate secure coding standard, five security questions in the code review checklist, Security Champions.