How to implement AppSec and DevSecOps so that security does not become a bottleneck for development: a roadmap, a Quality Gate and finding a balance between InfoSec and Dev.
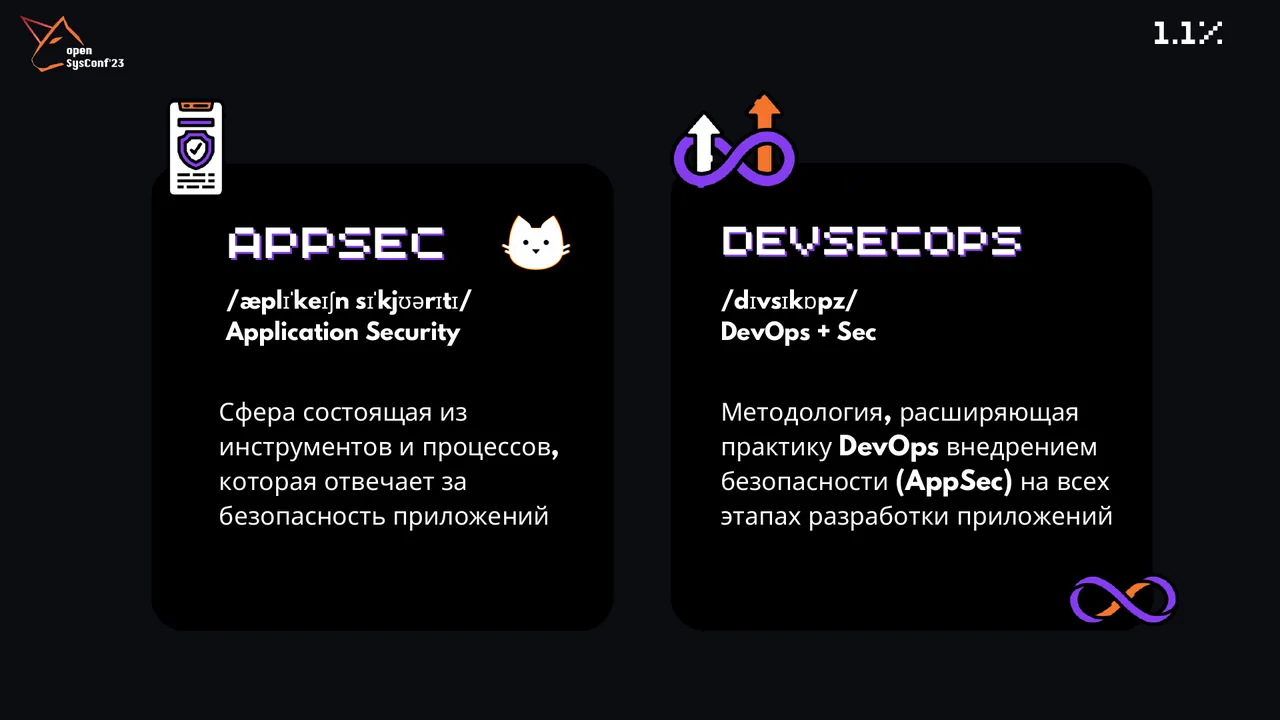
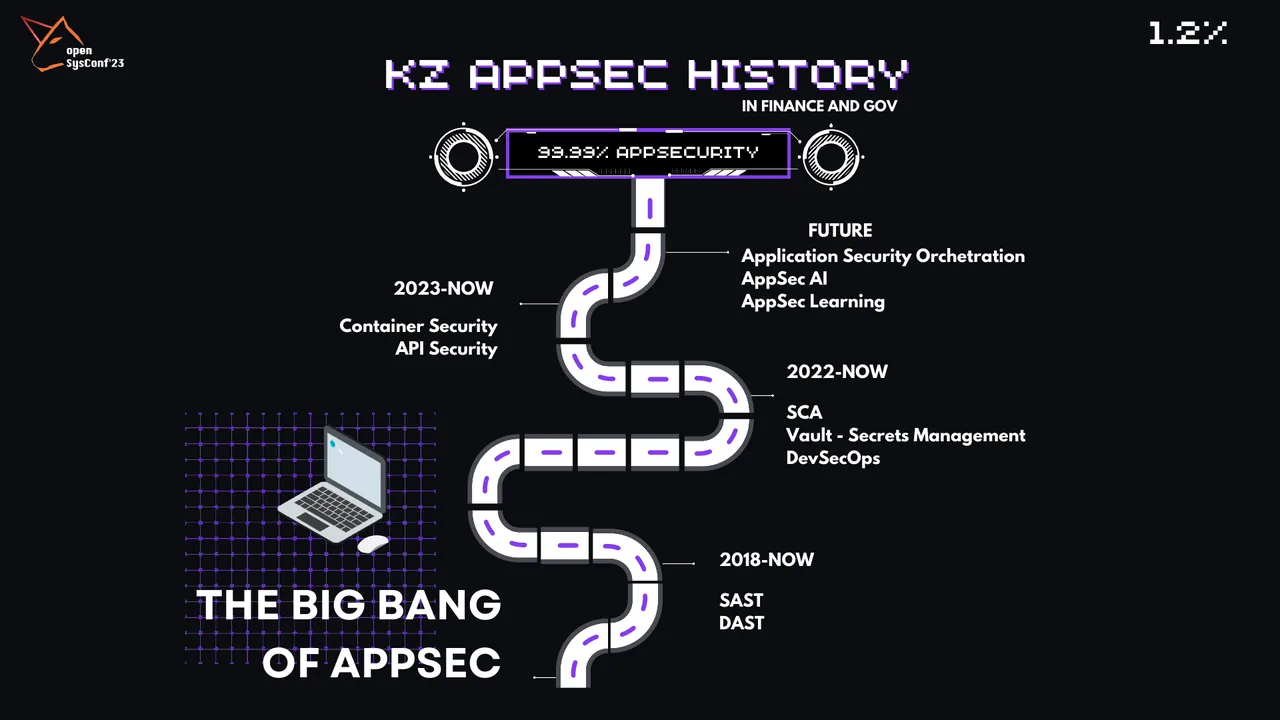
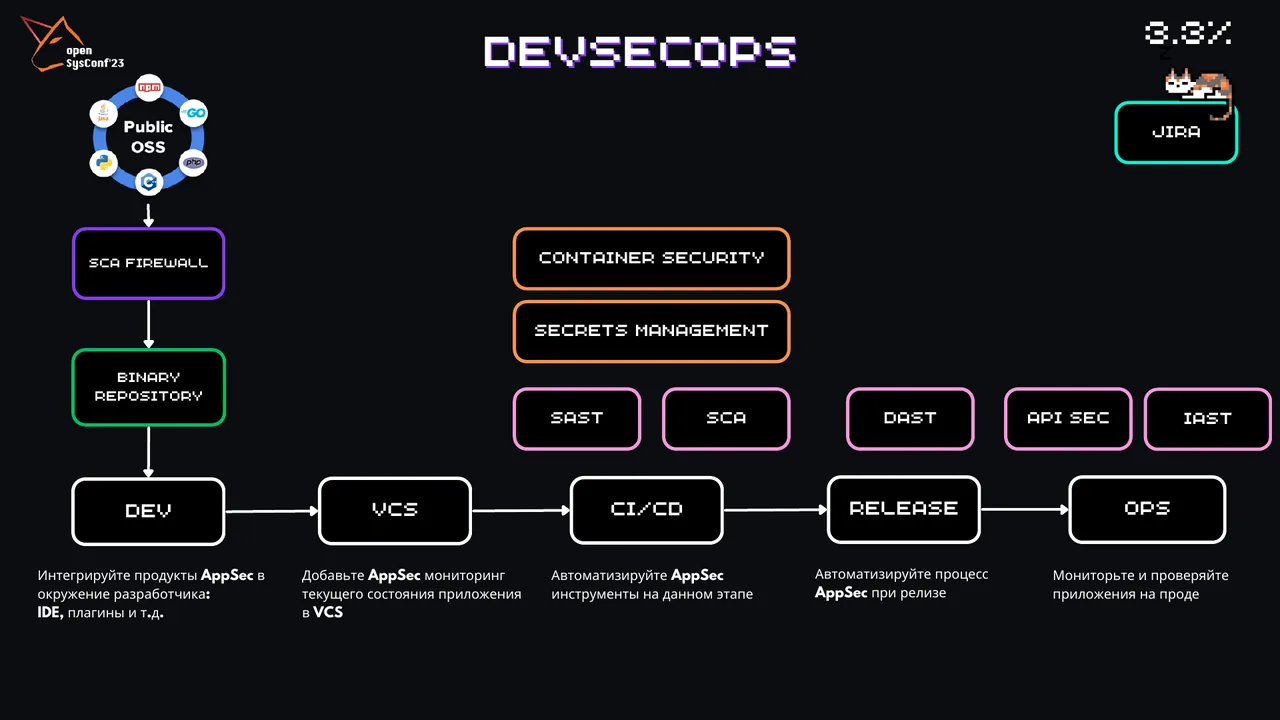
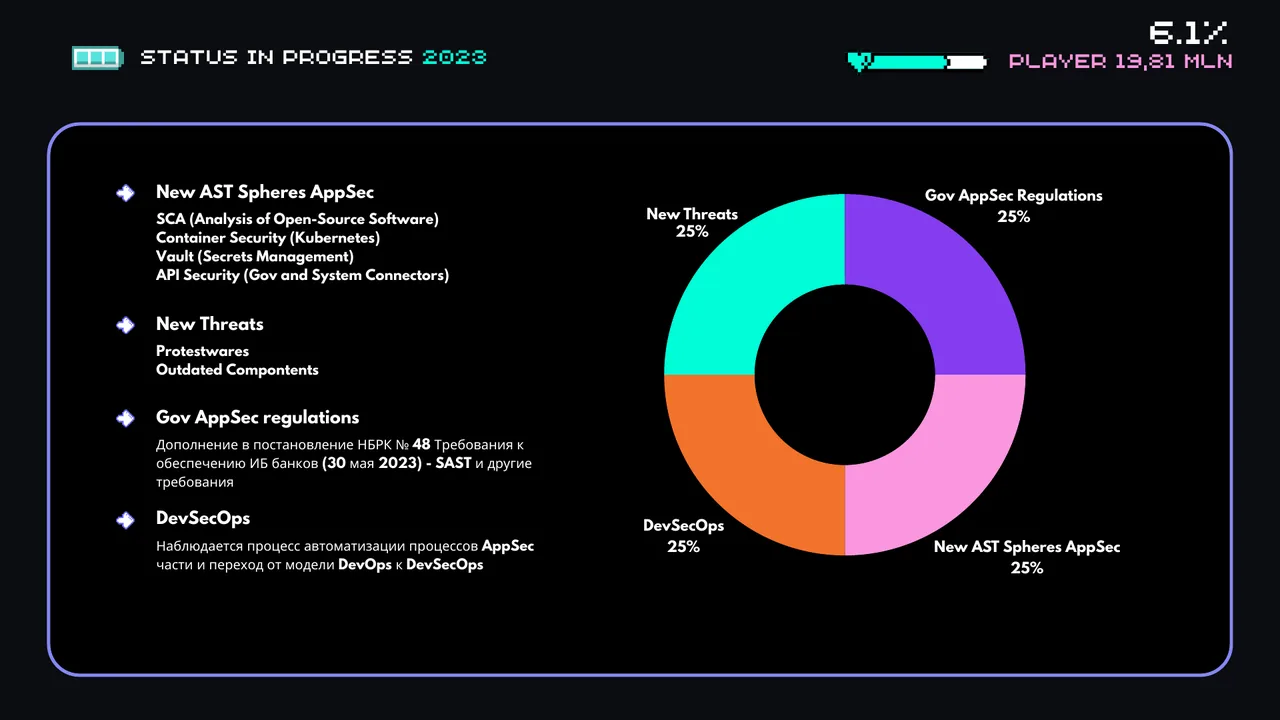
What AppSec and DevSecOps are and how application security developed in the financial and public sectors of Kazakhstan: from SAST and DAST in 2018 to SCA, secrets management, containers and API.
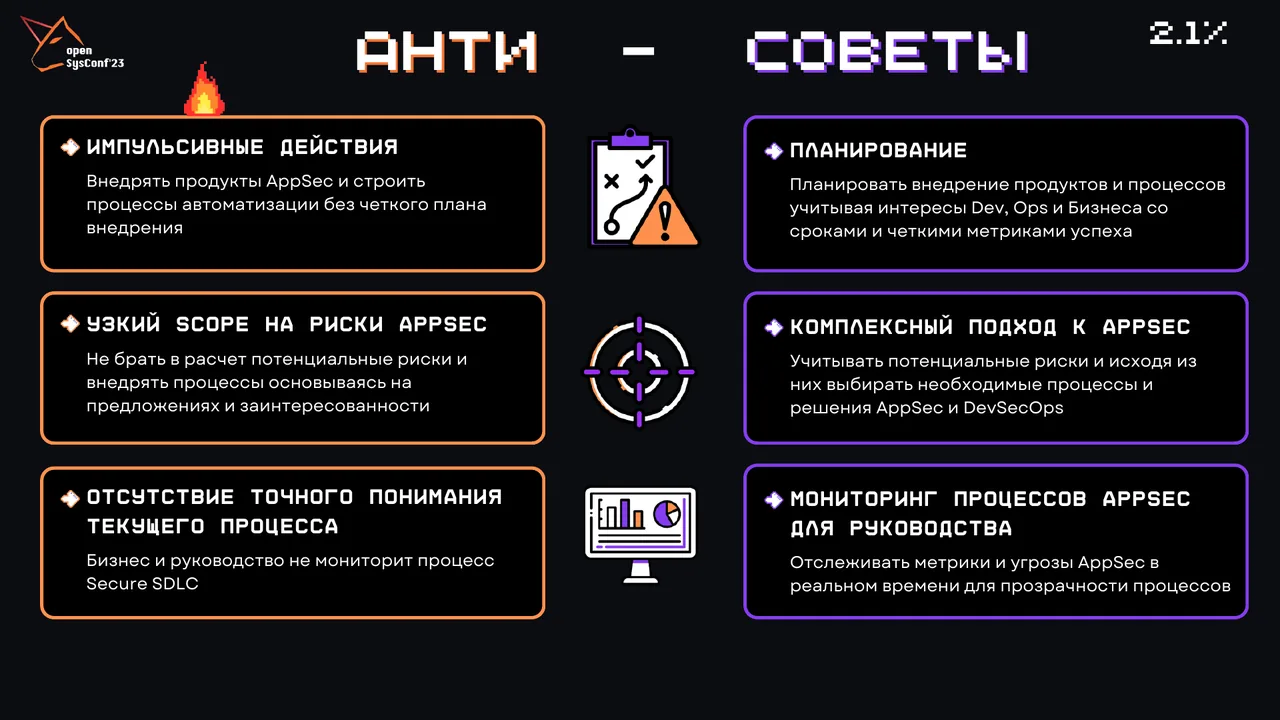
Anti-tips: implementation without a plan, a narrow view of risks, no process monitoring for management, and what to do instead.
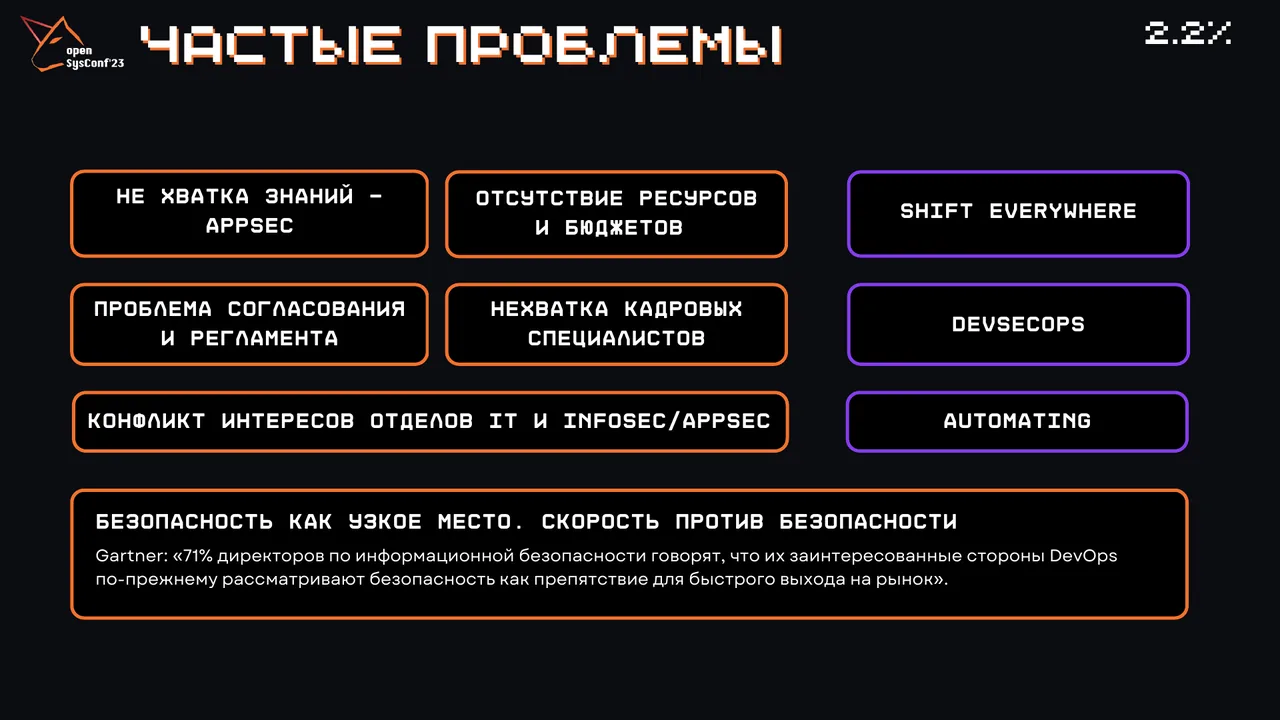
Common problems: lack of knowledge, people and budget, a conflict of interests between IT and InfoSec, security as a bottleneck.
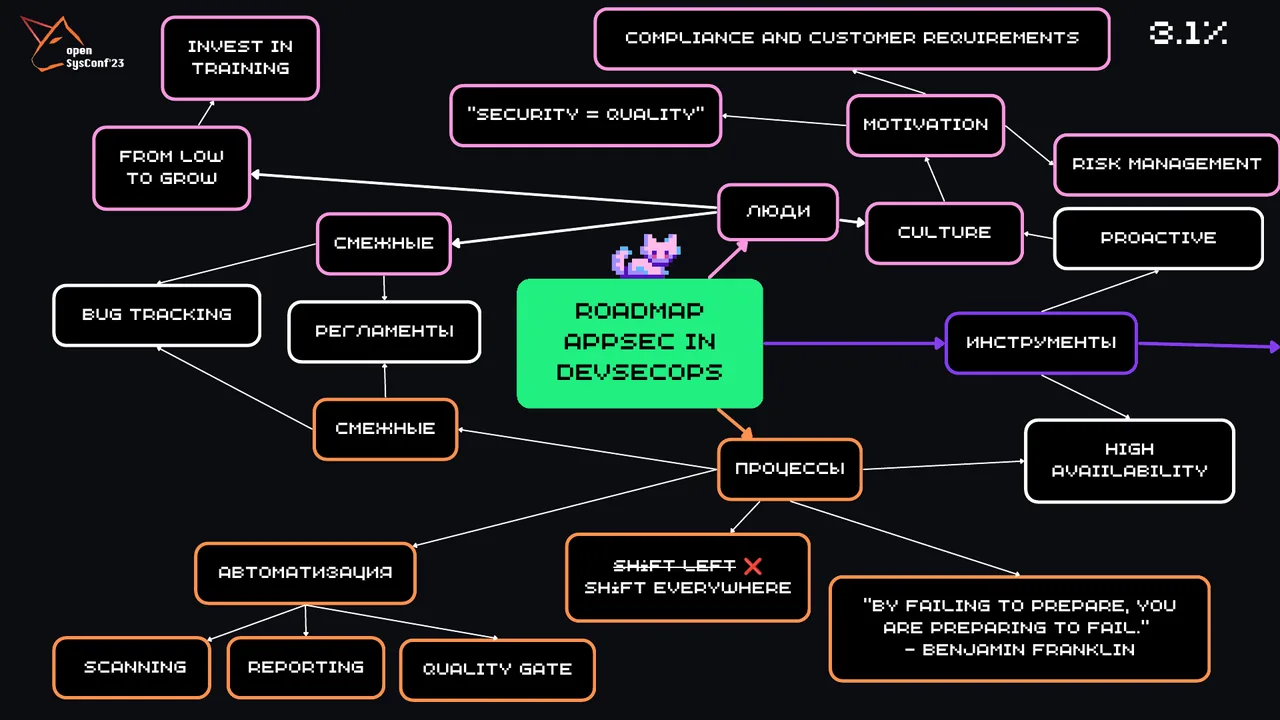
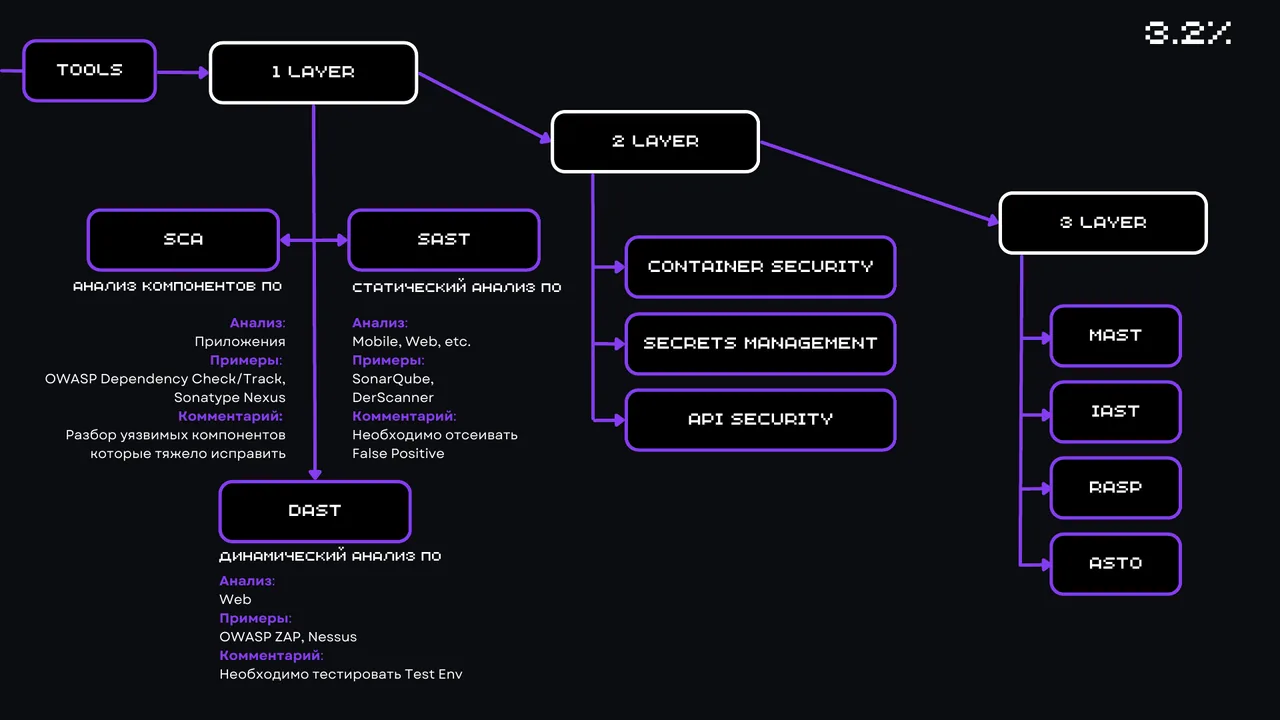
The AppSec roadmap in DevSecOps: people, processes, tools; three layers of tools, from SCA, SAST and DAST to IAST, RASP and orchestration.
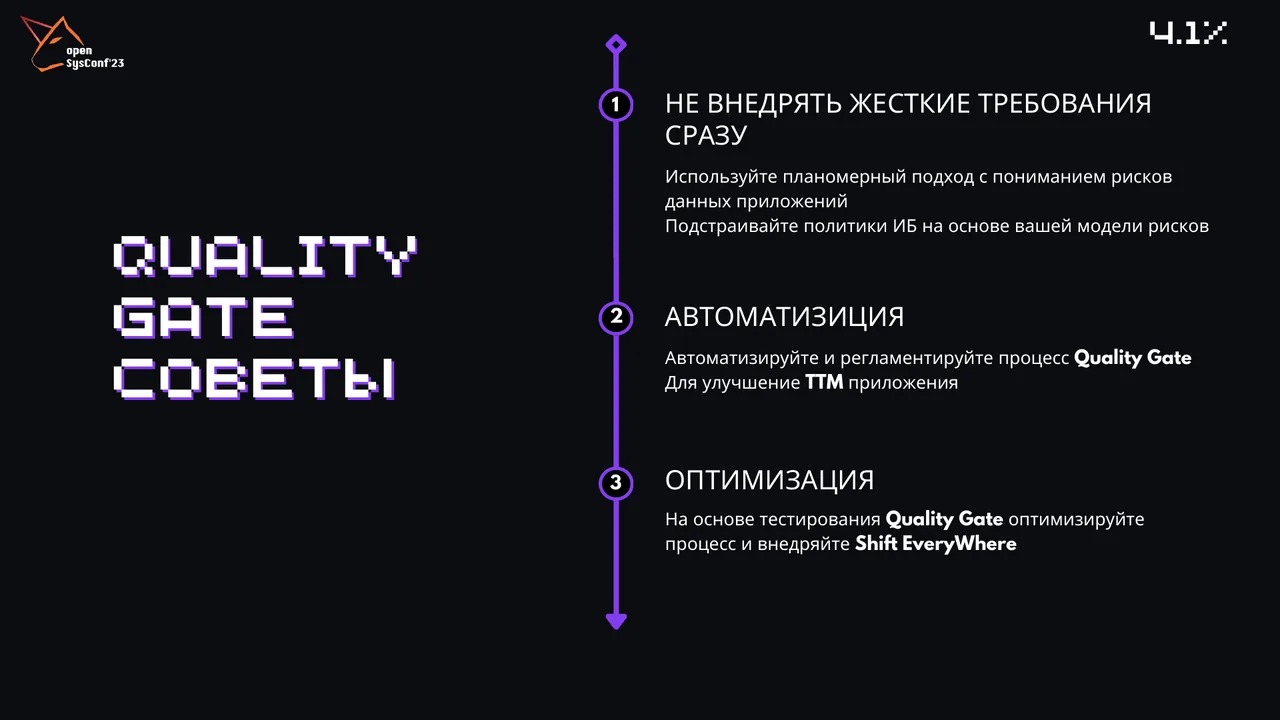
Quality Gate: do not introduce strict requirements right away, automate, take into account the interests of all participants and the specifics of business critical teams.
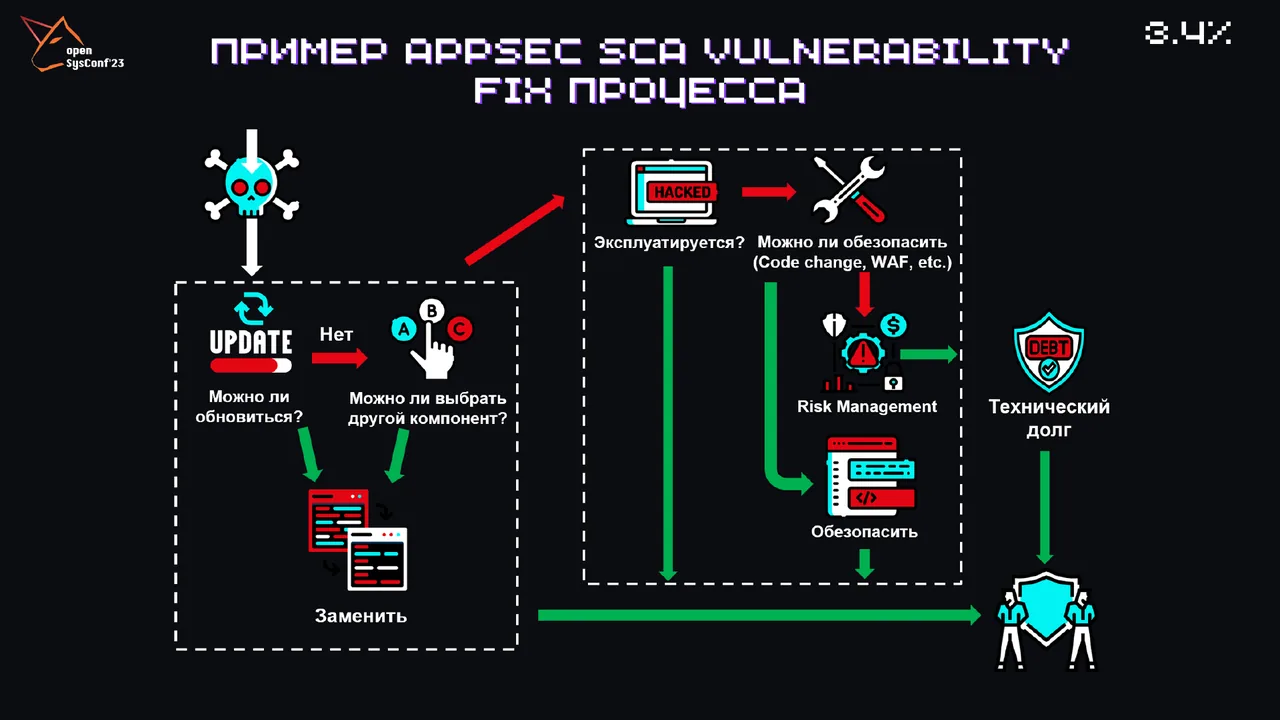
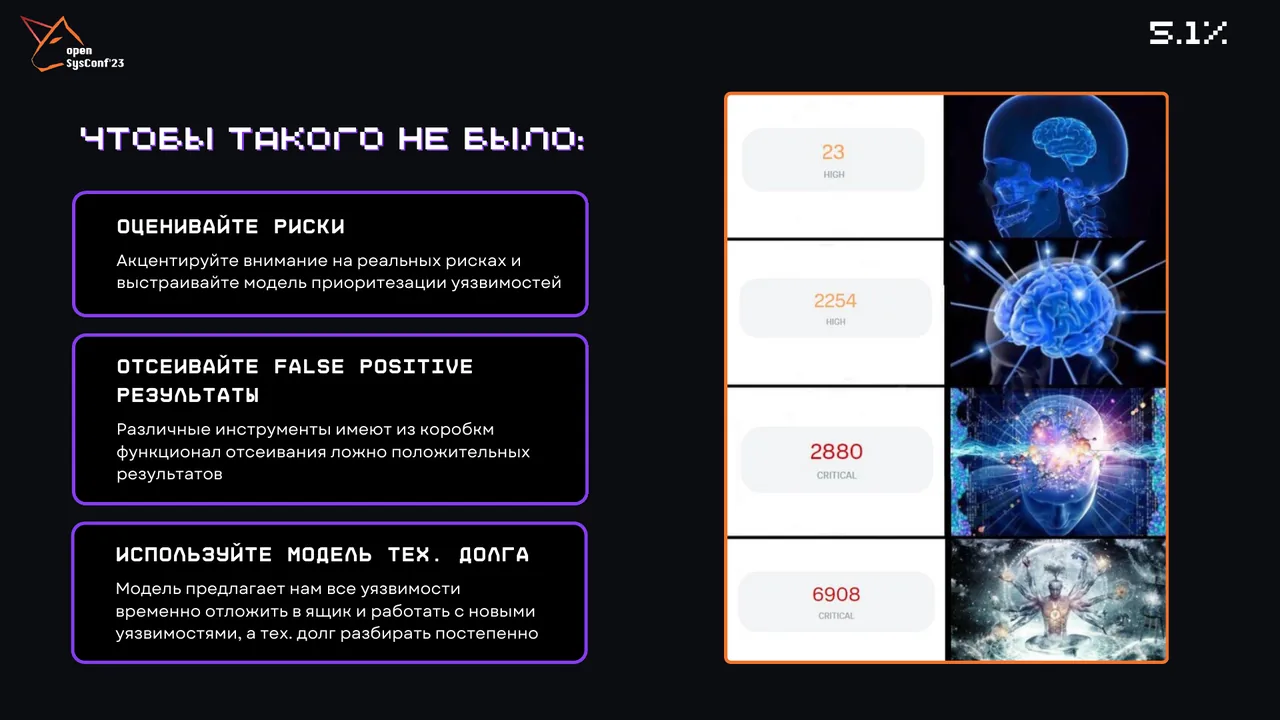
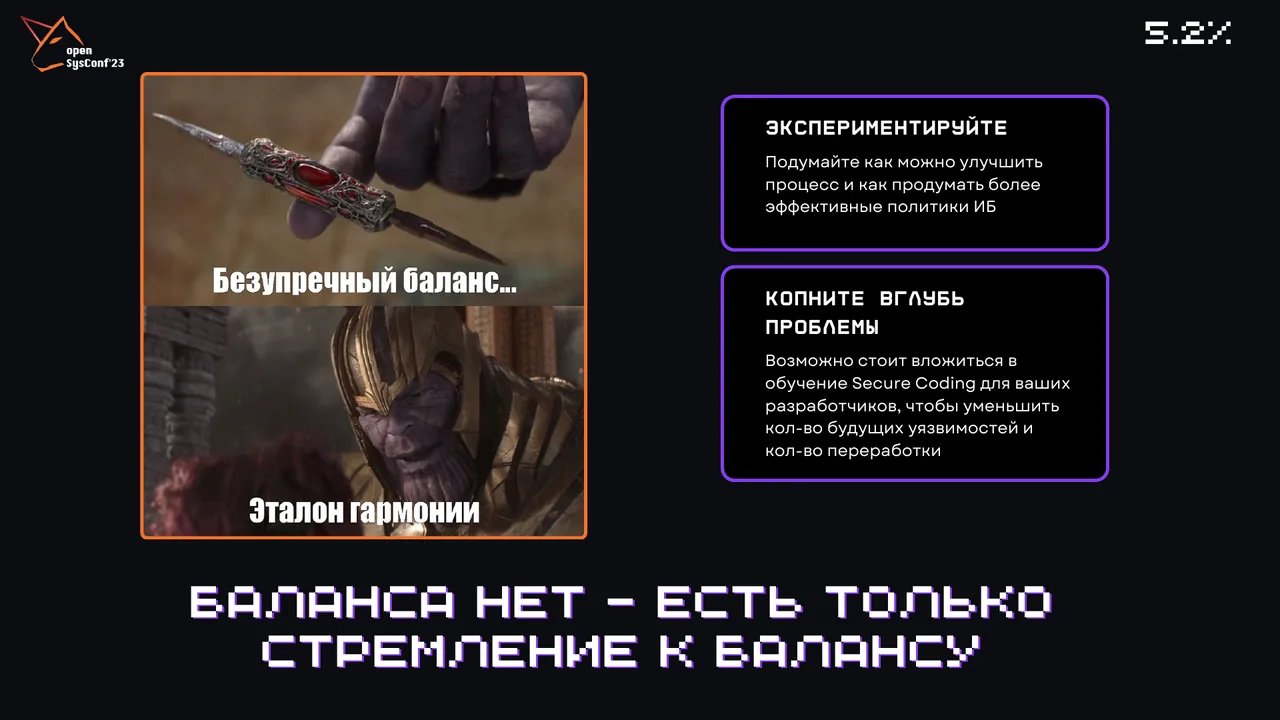
Balance between InfoSec and development: prioritization by real risks, filtering out false positives, a technical debt model, secure coding training.
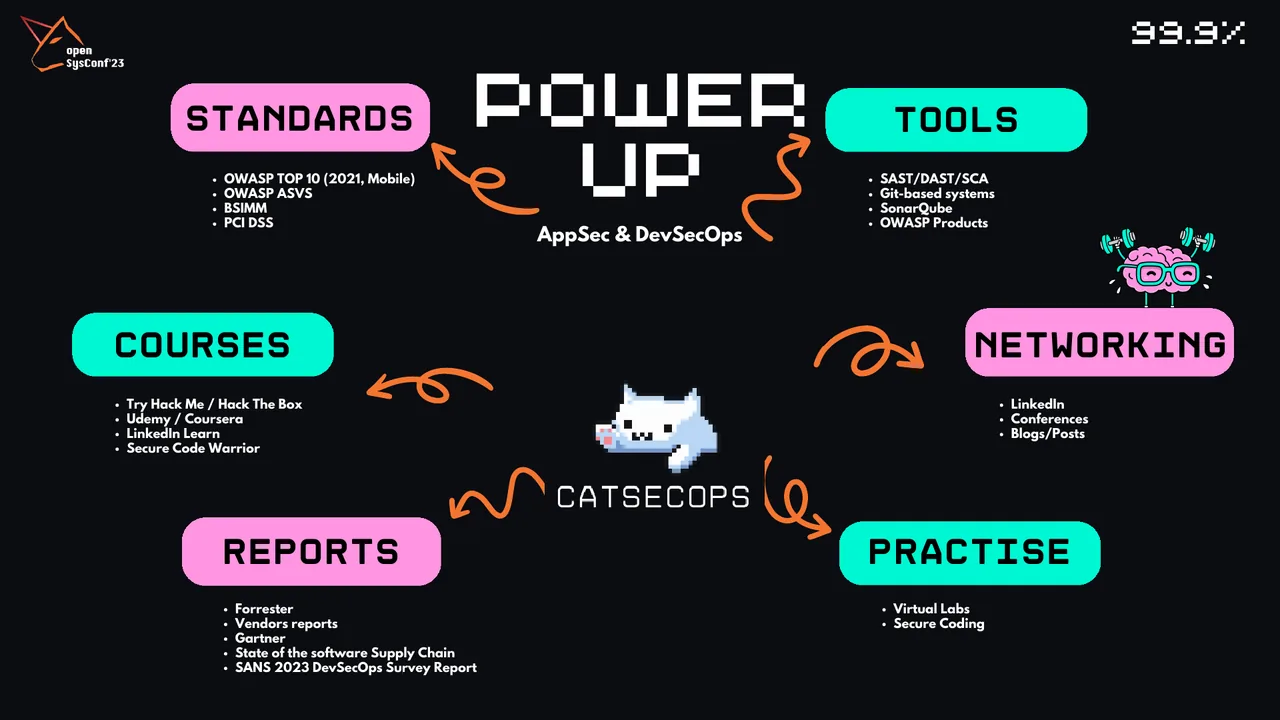
The trends of 2023 in Kazakhstan and what to study next: standards, courses, reports, practice.