Sonatype User Group Central Asia 2023 · Almaty · 2 November 2023
Why your software may already be hacked: a quick guide to component analysis
Third-party libraries are most of any application and a frequent entry point for attacks. How to find vulnerable components and build a process so they do not reach production.
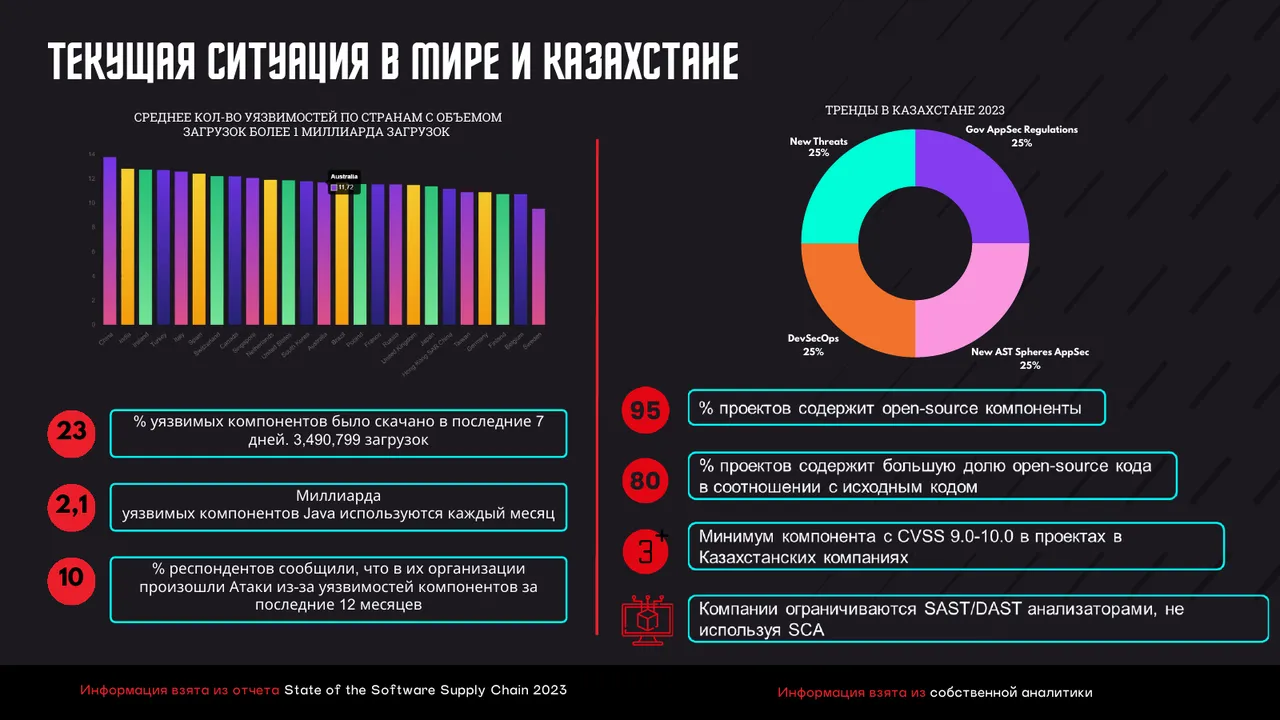
The situation in the world and in Kazakhstan according to the State of the Software Supply Chain 2023 report: vulnerable component versions continue to be downloaded en masse, attacks through dependencies have become routine.
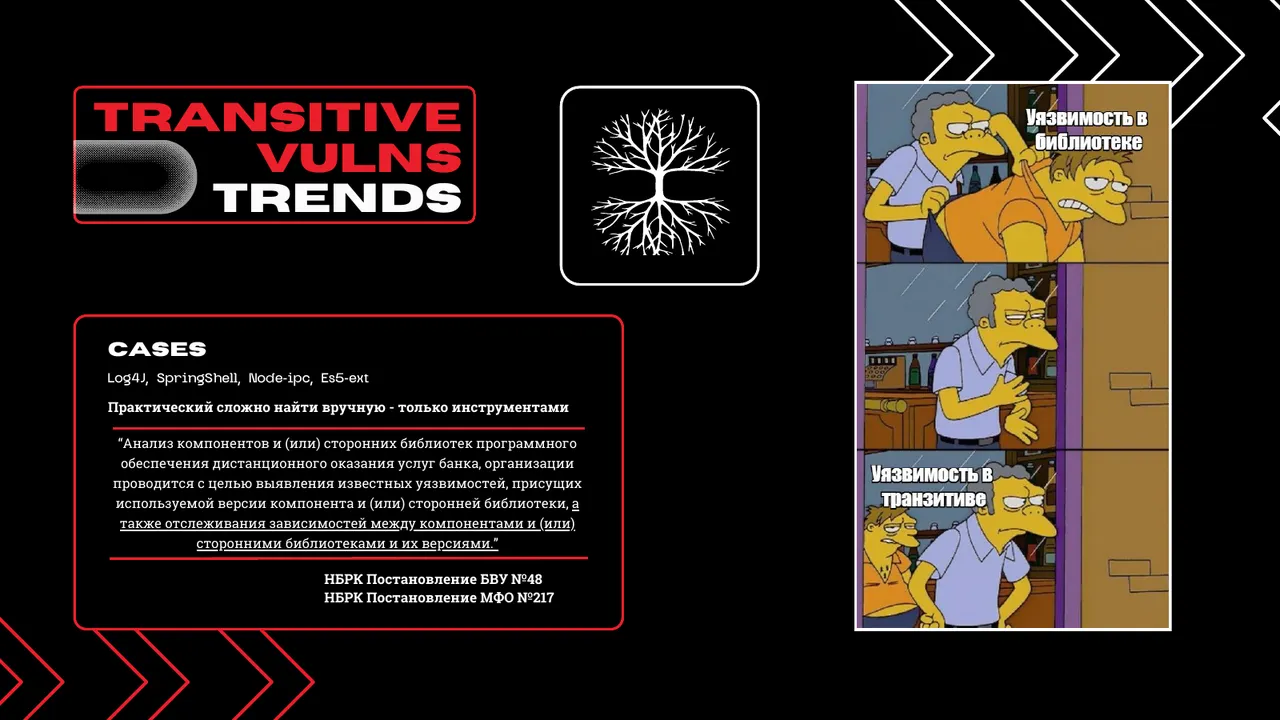
Why you cannot find them manually: transitive dependencies and the cases of Log4j, Spring4Shell, node-ipc, es5-ext.
Component analysis was directly required by NBK Resolutions 48 (now replaced by ARDFM Resolution No. 53) and 217 for remote service systems.
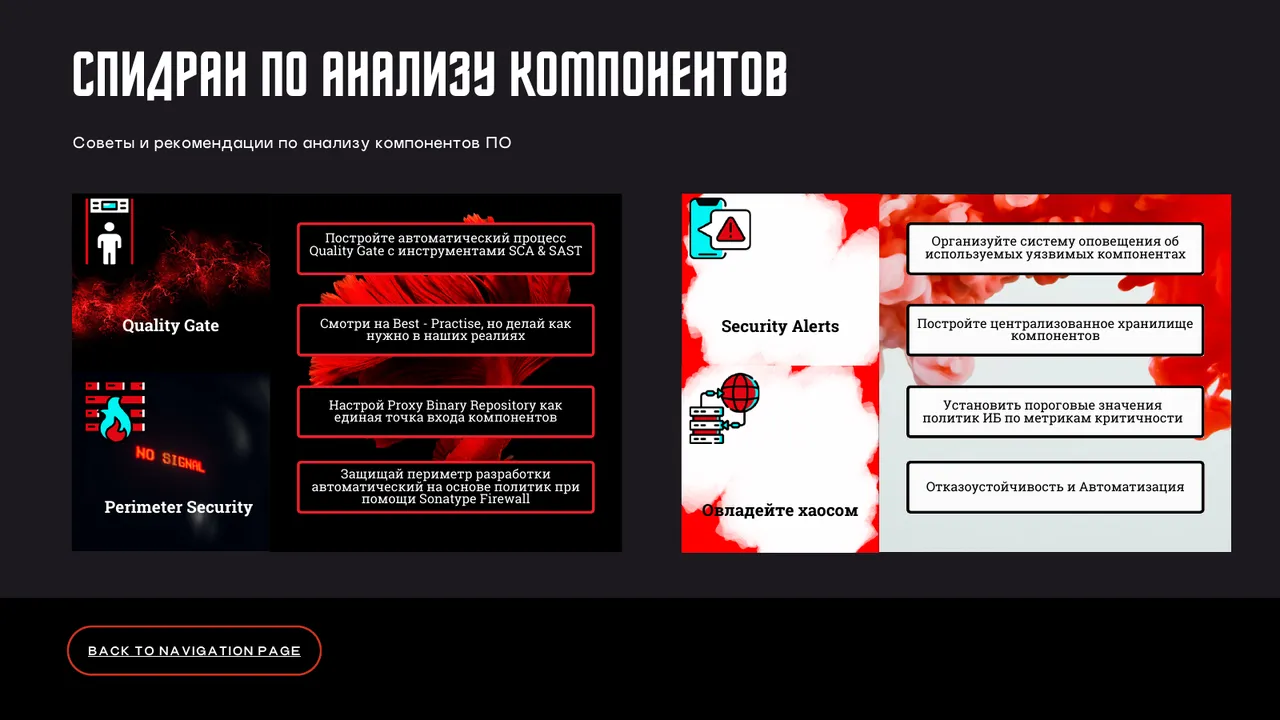
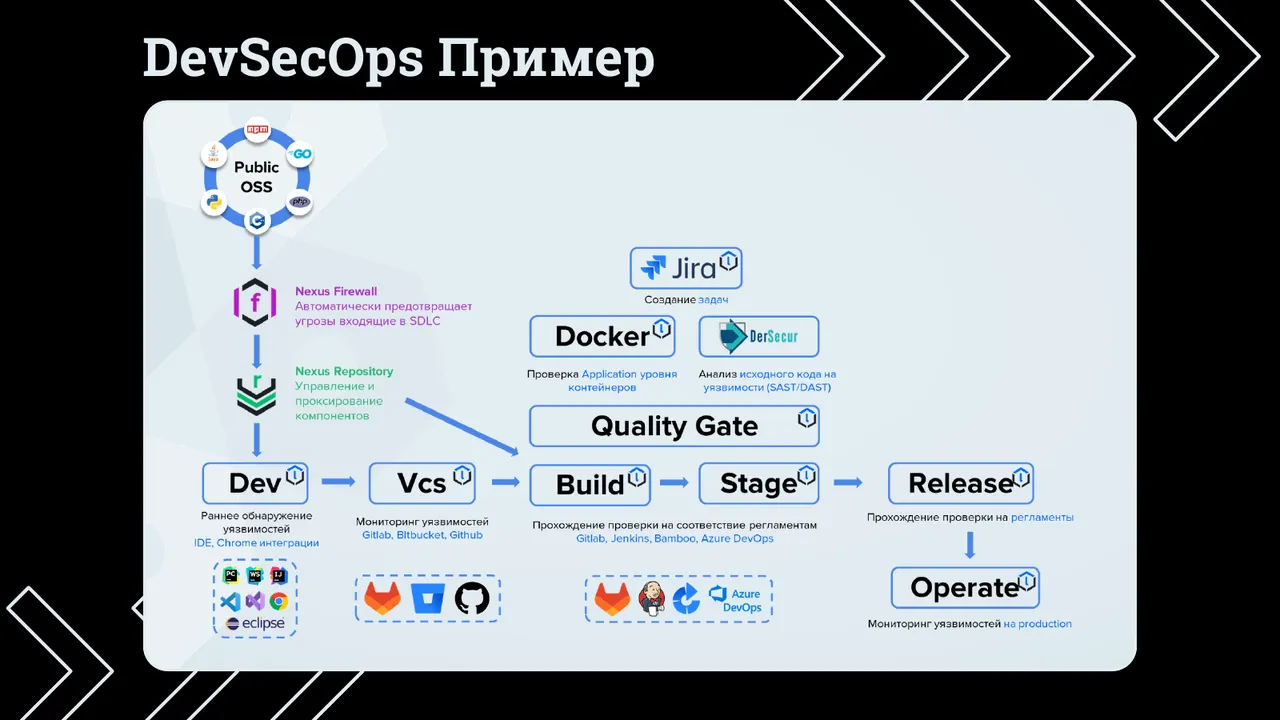
A speedrun through the process: a Quality Gate with SCA and SAST, a proxy binary repository as a single component entry point, alerts about vulnerable libraries, thresholds by criticality, protection of the development perimeter by policies.
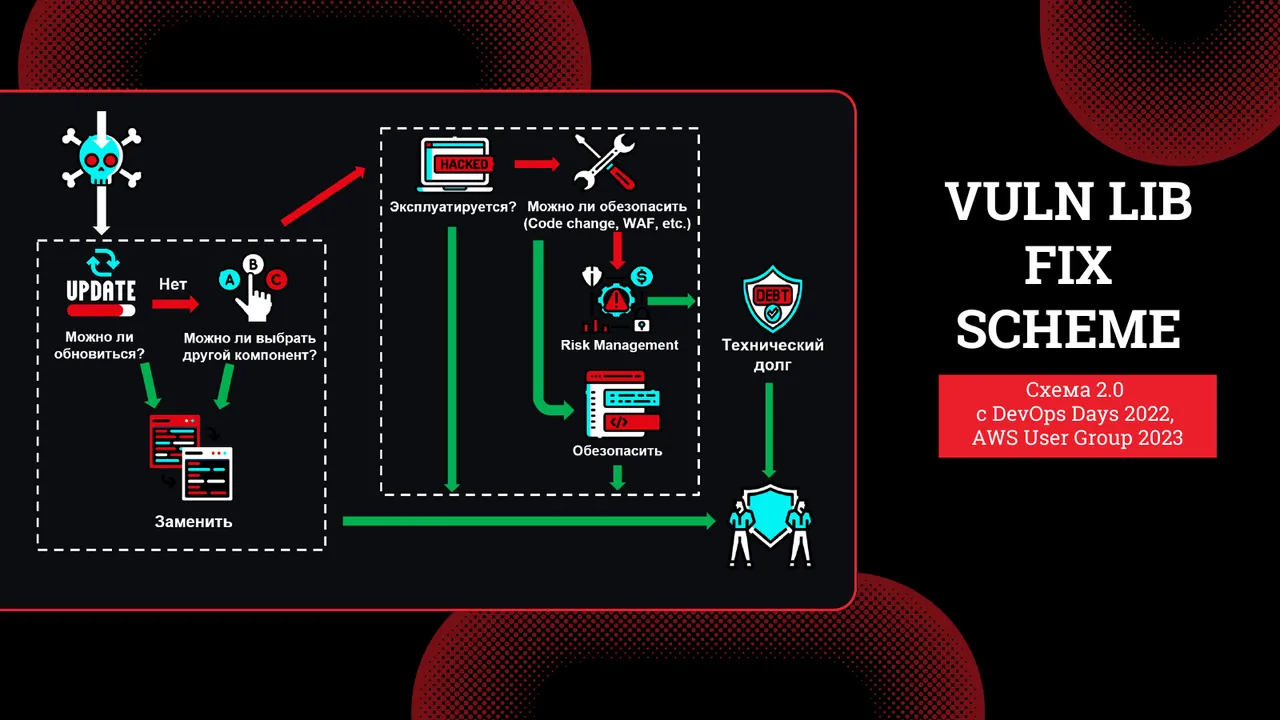
A scheme for fixing a vulnerable library: update, replace, close at the code or WAF level, or accept it as technical debt with risk management.
An example DevSecOps pipeline: checks from the IDE and repository to build, release and monitoring in production.